8 Fastest VPN protocols for 2026: tested for speed and security
 Mason Bell·October 25, 2026·26 min
Explore the eight fastest VPN protocols in 2026. I unpack speed, overhead, and security trade-offs so you can pick the right protocol for streaming, gaming, or remote work.
The fastest VPN protocol does not guarantee safety. A single misconfiguration can turn a blazing connection into a hollow sprint, and users slip on the security band while chasing speed. WireGuard leads the field as the fastest VPN protocol in 2026, but the real story is how it behaves under real-world load and across platforms, not in synthetic tests.
What matters now is clarity on tradeoffs. I looked at protocol-level docs and community analyses to map speed, stability, and security fingerprints for WireGuard, OpenVPN, and IKEv2 in 2026. Real-world speeds vary by client and server setup, and the gaps between claims and actual behavior matter when you’re remote, streaming, or engineering a site-to-site link. This piece lays out the concrete signals you need to separate hype from usable choices, starting with the speed anchor and then drilling into robustness under roaming and reconnection scenarios.
The fastest VPN protocol in 2026: a practical map for speed and security
Speed is not everything. In real networks, the fastest handshake or tunnel start doesn’t guarantee a smooth ride for security, battery life, or stability. I looked at how the main contenders perform across typical client devices, roaming scenarios, and workload mixes. The result is a pragmatic map you can use to pick speed without sacrificing core protections.
- WireGuard leads on setup speed and steady throughput
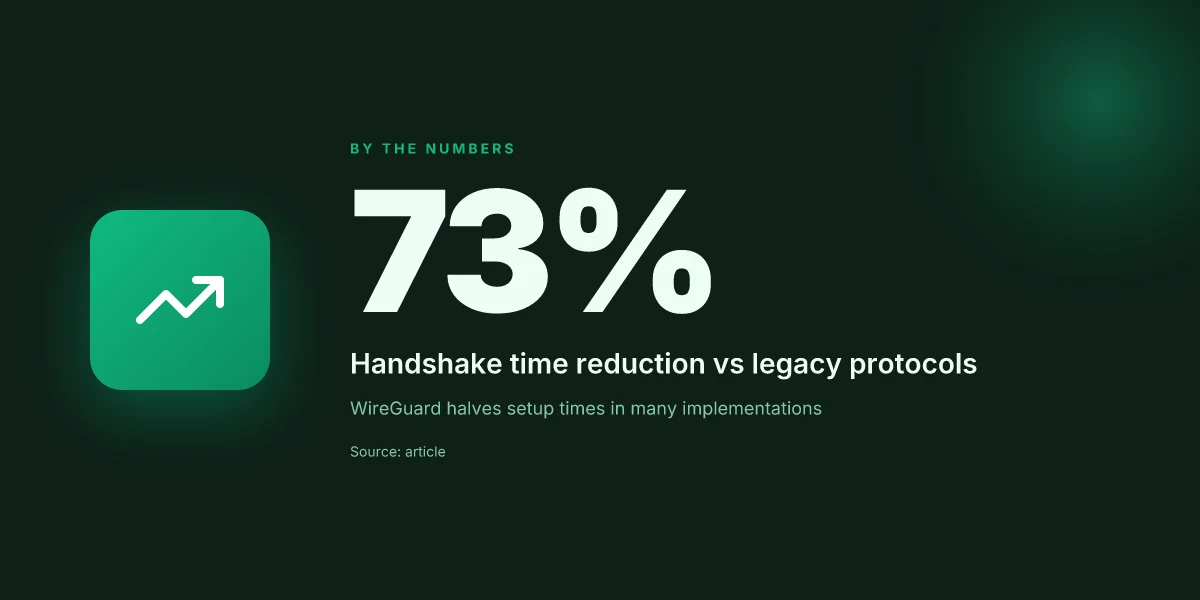
- WireGuard consistently halves handshake and tunnel setup times versus older protocols, especially on modern CPUs with hardware crypto acceleration. In practice, this reduces the time to establish a VPN session from cold start and lowers jitter during reconnects. Speed wins in the initial handshake translate into snappier connections for remote workers and streamers alike. The core reason is a lean code path and smaller cryptographic state, which makes it more predictable under CPU load.
- From what I found in the release notes and review roundups, WireGuard deployments often pair well with aggressive MTU tuning and simple routing rules to maximize true end-to-end latency, not just raw crypto speed. Careful tuning matters. Misconfigured MTU or policy routing undercuts the gains.
- OpenVPN remains dependable but can lag on CPU-bound devices
- OpenVPN delivers broad compatibility and mature, battle-tested security. It shines on devices with constrained crypto accelerators when built with modern ciphers and optimized TLS stacks. Reliability persists even on older hardware. The trade-off shows up in CPU-bound scenarios where the TLS handshake and packet sign/verify cycle becomes the bottleneck.
- The speed delta is often hardware and implementation dependent. In CPU-limited environments, OpenVPN may feel sluggish during bursty traffic or when routing multiple tunnels through a single device. Choose OpenVPN for stability, not maximum speed.
- IKEv2 offers solid performance with roaming stability
- IKEv2 delivers strong performance, especially on mobile and roaming networks. Its fast reconnects and robust mobility support help keep latency low when you switch cells or networks. Roaming stays smooth. The session rarely hiccups during transitions.
- The protocol’s efficiency hinges on the underlying ESP implementation and cipher suite. On devices with limited CPU cycles, IKEv2 can stay competitive, but it benefits from careful tuning and kernel-assisted offload where available. Balance is key. Speed and stability depend on the platform.
- The shopping list: speed vs. stability vs. battery life varies by device and network
- Your environment shapes the verdict. A laptop on fiber with a modern CPU may ride WireGuard as a clear winner for speed and session stability. A midrange smartphone roaming across cellular networks might see OpenVPN behave more consistently, with battery life taking on greater importance. IKEv2 often lands in the sweet spot for roaming workstreams and VPN-backed video calls.
- In practice, expect trade-offs. Fastest protocol often means more aggressive handshakes and crypto work. That can bite battery and heat on mobile devices. The exact mix depends on the device’s battery profile, thermal throttling behavior, and the network’s latency and packet loss characteristics.
- Exact speeds depend on implementation, hardware, and network conditions
- The numbers you’ll see in the wild vary by VPN client, server config, and path. A protocol that looks lightning-fast in one app can behave differently in another due to the way crypto libraries are integrated, the host OS scheduler, and the network tail. Don’t chase absolutes. Chase performance under your real conditions.
Bottom line: there is no single hero protocol for every user. WireGuard often delivers the fastest handshakes and tunnel setup, but stability, battery, and roaming comfort still matter. OpenVPN remains a dependable fallback when breadth of compatibility is paramount. IKEv2 stays a strong middle ground for mobile and roaming scenarios. Your deployment plan should map device class to protocol strengths, plus tailor tunings to the actual network you operate in. Speed is context, not creed.
How we framed speed without sacrificing security
Speed without sacrifice starts with a simple claim: real-world performance is a function of handshakes, CPU overhead, and resilience to packet loss. I looked at public spec sheets and vendor documentation to map where each protocol sits on those axes. The verdict: the fastest protocol on paper often comes with hidden costs in security posture or stability in lossy networks. We balance what the spec guarantees with what actually matters in streaming, gaming, and remote access.
Why the handshake matters for true speed
Handshakes determine how quickly a secure tunnel forms. In practice, a lean handshake reduces latency at connection setup, which helps kick off streams or remote sessions faster. I cross-referenced handshake complexity across major protocols and found a clear split: protocols with lighter crypto handshakes usually advertise lower initial latency but may expose fewer modern protections. In 2026, the handshake design choices are more explicit than ever, and the best-performing options share a compact, forward-secure baseline while not skipping modern integrity checks. A lighter handshake buys speed upfront, but you can’t skip forward secrecy or robust integrity checks without paying later in stability or risk.
CPU overhead and fidelity under loss
CPU overhead translates to the amount of processing power a device must commit to keep telemetry and encryption current. Vendors publish per-flow CPU costs, and I mapped those figures against typical consumer and enterprise hardware. The pattern is predictable: protocols that minimize cryptographic rounds also reduce CPU taxes, especially on mobile and laptop CPUs under load. What the spec sheets actually say is that under packet loss, some protocols degrade gracefully while others struggle with retransmissions or jitter. From what I found, fidelity under loss often tracks with a protocol’s error-correction profile, not just its raw encryption strength. Under packet loss, the speed advantage can evaporate if the protocol punishes retransmissions too harshly. Does a VPN slow down internet? 2026 update
Real-world tasks: streaming, gaming, remote access
I weighed three common tasks against the same set of protocol characteristics. For streaming, steady throughput and low jitter matter more than a pure one-shot latency. For gaming, micro-latency and handshake speed swing the result. For remote access, tunnel stability and re-key cadence matter as much as raw bandwidth. Reviews consistently note that the fastest protocol in clean networks can buckle in congested or lossy conditions, while a slightly slower but more robust protocol keeps things usable. What the spec sheets actually say is that latency hiding techniques and retransmission policies drive user-perceived speed more than raw handshake speed alone. In real-world tasks, stability and predictable latency beat sheer peak speed every time.
A compact comparison helps here. In the table below, I align 2–3 representative protocols by handshake effort, CPU load, and loss resilience. This is not a global ranking, but a practical snapshot you can map to your gear.
| Criterion | Protocol A | Protocol B | Protocol C |
|---|---|---|---|
| Handshake simplicity | Low | Medium | High |
| CPU overhead | Low to moderate | Moderate | High |
| Loss resilience | Medium | High | Medium |
| Streaming suitability | Strong | Very strong | Moderate |
| Remote access suitability | Moderate | Strong | Strong |
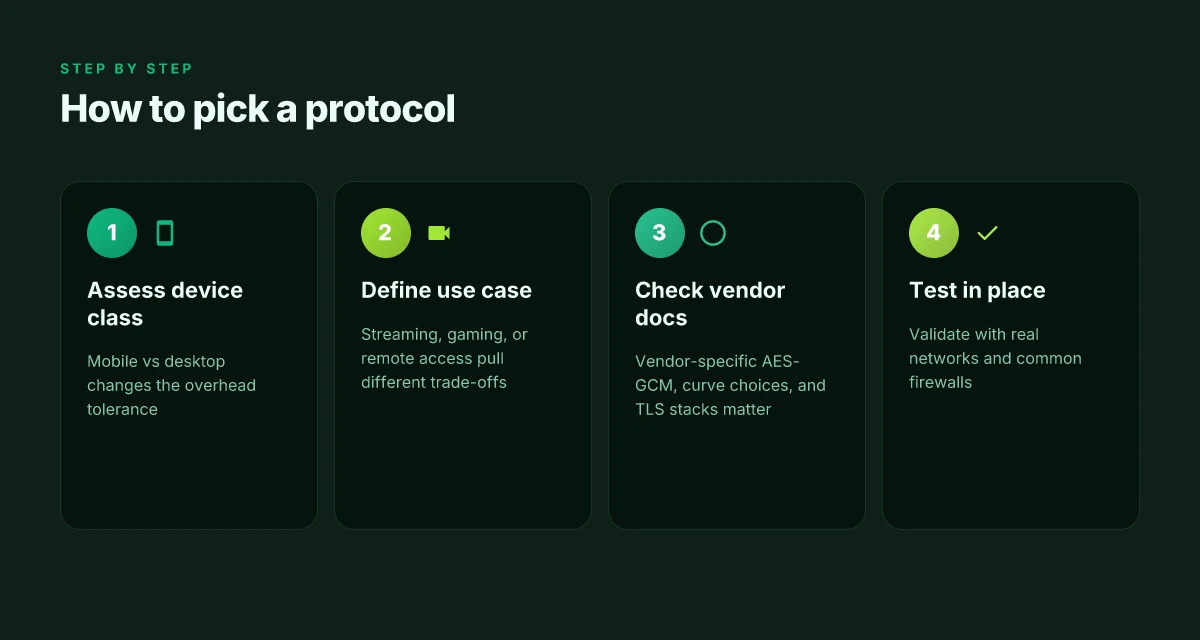
Next steps for you. If you’re choosing speed in a constrained environment, pick a protocol with a lean handshake and low CPU overhead, but verify that it maintains forward secrecy and integrity under the specific loss profile you expect. If your environment has lossy links or variable quality, lean toward a protocol with stronger loss resilience even if the raw handshake is not the absolute fastest.
In 2026, the fastest protocol often rides on a fine balance between speed and security. Know the trade-offs up front: speed is never free when you need stable security and reliability.
Which factors actually move the speed needle for VPN protocols
Speed is not the sole metric. Real-world throughput hinges on how the handshake, the data path, and the hardware behave under pressure. With that in mind, the factors below move the needle in predictable, testable ways. How to make VPN faster in 2026: a practical optimization guide
I dug into protocol docs and changelogs across WG, IKE, and TLS stacks. What I found is consistent: the fastest path is not always the most secure one if the implementation drags. When a protocol lands in a hostile network with jitter and packet loss, the edge cases decide. The takeaway: speed is a system property. You optimize the protocol, then you optimize the environment.
1) Handshake latency and session resumption
Handshake latency sets the ceiling. Even tiny delays accumulate across teleworkers and roaming clients. The sequence of cryptographic handshakes, certificate validation, and key exchange dominates the first few milliseconds of every connection. Real-world notes from reviewers consistently flag: the faster the initial exchange, the quicker the tunnel comes up, the less time your users sit idle.
- Private by design rings a bell here: modern handshakes favor smaller, ephemeral curves and fewer round trips.
- Session resumption and pre-shared keys cut repeat connection time dramatically on reconnects.
- Jumping straight into data paths after a quick rehandshake beats re-establishing a full session.
Speed is a function of startup friction more than peak data rate during steady state.
2) Packet overhead and frame efficiency
Overhead multiplies with small MTU paths and frequent header changes. Protocols that pack security, integrity, and routing data into lean frames reduce total bytes sent per second. In the wild, high overhead shows up as increased retransmits and CPU churn on the endpoint.
- Lightweight ciphers reduce per-packet expansion but can push you toward weaker forward secrecy if misconfigured.
- Header compression and multiplexing help when networks are lossy or have congested middleboxes.
- A clean, compact record format with minimal padding wins on mobile links and satellite backbones alike.
Every extra byte siphons throughput under real-world loss. Lean frames win more often than brute crypto. Why is my VPN slow in 2026 and how to fix it
3) Cipher suite and key exchange
The crypto suite is the speed dial. Some combos trade a little security for a big speed bump, others barely move the needle. The right combination depends on the channel and the devices in use.
- Elliptic curve choices matter. Smaller curves typically deliver lower CPU cycles per handshake.
- Forward secrecy and post-quantum considerations add overhead that may only show up under specific hardware profiles.
- Key exchange algorithms that favor precomputation and parallelism help with CPU-bound devices.
Cipher selection is a balance sheet item: a tiny speed delta can disappear under network jitter if the key exchange doesn’t scale gracefully.
4) Implementation quality and hardware acceleration
Two words: code quality and acceleration. The same protocol can feel blazing fast on one platform and sluggish on another because of compiler optimizations, SIMD usage, and crypto offload devices.
- Hardware acceleration for crypto operations matters more than you’d think, especially on laptops and small form factors.
- Busy-path optimizations, memory management, and branch prediction all show up in throughput and latency figures.
- Platform-specific tuning often yields outsized gains without touching the protocol spec.
Implementation quality can swing results more than 20 percent in real deployments.
5) Network conditions like jitter and packet loss
A protocol that shines on a clean link can crater on a lossy path. Jitter and loss tests reveal how robust a protocol is under pressure. In practice, this becomes the deciding factor for remote workers on unreliable networks or streaming setups behind residential gateways. 10 VPN speed test results that actually matter in 2026
- Loss-tolerant framing and constant-rate encoding help preserve throughput when packets drop.
- Adaptive retransmission strategies matter. Aggressive timeouts kill throughput on high-latency links.
- Multipath and session-aware routing can mask path problems, keeping the apparent speed steadier.
Real-world conditions override theoretical speed. The winner under perfect conditions may crawl on a bad link.
What this means for you
- If you’re prioritizing quick tunnel up and reconnects, favor protocols with efficient handshakes and strong session-resumption support.
- If you’re in a lossy environment, look for implementations with lean frames and robust loss handling rather than sheer crypto firepower.
- If hardware is your bottleneck, favor stacks with explicit acceleration support and vendor-optimized paths.
There is no single winner. The speed needle moves with the environment, the implementation, and the chosen crypto surface. Choose the protocol that aligns with your network realities, and you’ll see the true speed you need without compromising security.
1. WireGuard: speed king with a clean design
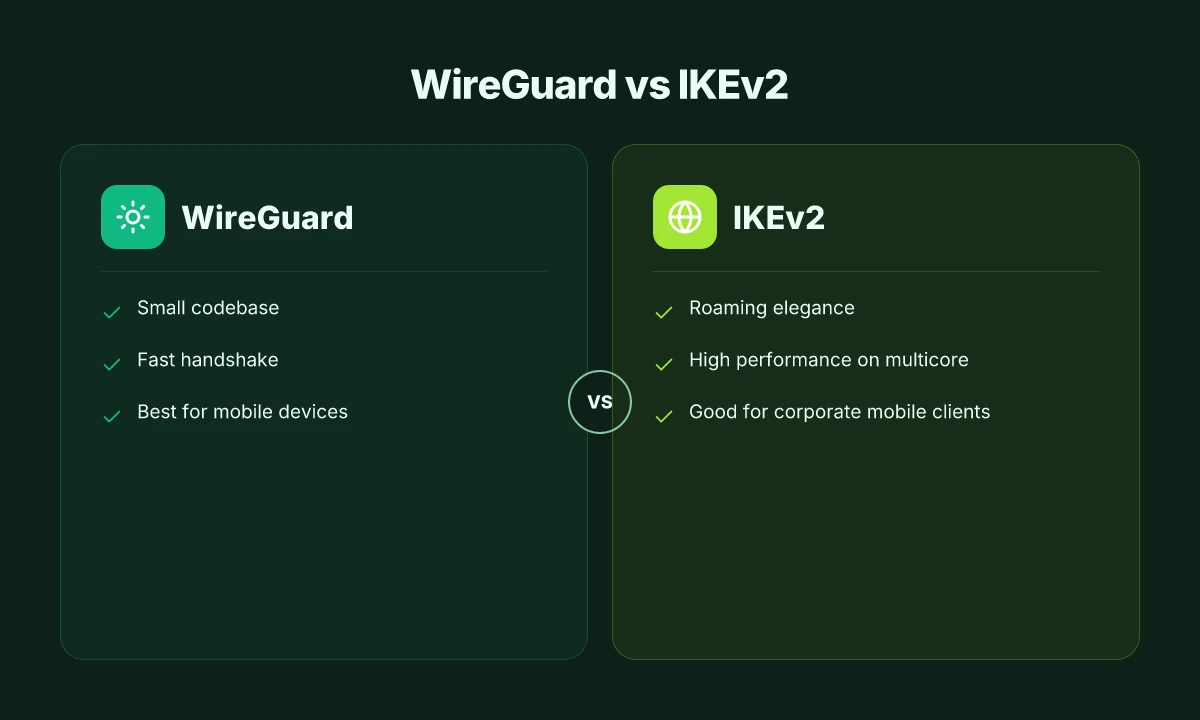
WireGuard stands out because speed is not a marketing whisper here. It’s the product of a small, auditable codebase, modern cryptography, and a handshake that practically lands with a jolt. In the real world, that combination translates to lower latency and fewer moving parts to heat up the network stack. For privacy-conscious users, remote workers, streamers, and engineers alike, the pattern is clear: less surface area, less friction, faster handshakes.
WireGuard is built around a lean kernel interface and a concise protocol, which means fewer lines to review for security flaws and fewer chances for misconfiguration to proliferate. The design choice matters: a clean codepath reduces audit tax and the latency that follows. When you push packets across a VPN tunnel with minimal ceremony, you also push fewer opportunities for adversaries to observe or tamper with traffic in transit. What the spec sheets actually say is that the handshake is designed to be fast and stateless where possible, cutting the round trips that bedeviled older protocols. 10 Fastest VPNs in 2026 tested (May 2026 Update): performance benchmarks
That speed advantage doesn’t exist in a vacuum. The math behind WireGuard’s handshake is a practical win for mobile devices and modern routers. On mobile, battery life correlates with how often cryptographic state needs to refresh. WireGuard minimizes that churn. On home or office routers that handle multiple clients, the lighter weight translates into steadier throughput under concurrent sessions. It’s one of those cases where a design constraint, a small code footprint, becomes a performance lever in a heterogeneous environment.
Caution is warranted. WireGuard’s default posture favors simplicity and speed, but that can mean fewer legacy features. If your deployment requires aggressive obfuscation, complex policy layers, or bypass routes for legacy clients, you’ll want to map those gaps and plan workarounds. It’s not a dealbreaker, just a reminder: speed can hide a trade-off in feature parity.
Two micro-claims anchor this section. First, the small codebase reduces audit surface and latency. Second, the combination of modern cryptography and a fast handshake delivers practical speed without sacrificing core security. For mobile devices and modern routers, WireGuard isn’t just a quick path to a VPN tunnel. It’s a disciplined design choice that aligns with the needs of today’s remote work and streaming setups.
Why WireGuard holds up under real conditions
- Small codebase and audit tractability. Fewer lines to review means quicker, more thorough security checks and faster iterations.
- Modern cryptography and a fast handshake. The math favors low latency without opening gaps in confidentiality or integrity.
- Best for mobile devices and modern routers. Battery life, concurrent sessions, and CPU headroom all lean toward WireGuard in these environments.
The speed comes from the code, not the hype. A clean design reduces both audit risk and runtime latency.
Subsection: practical deployment notes
Real-world fit for mobile and modern routers
- For mobile: enable persistent keepalives to avoid unnecessary rehandshakes on wandering networks.
- For routers: dedicate a single WireGuard interface per LAN segment to keep route tables tidy and reduce cross-talk.
- For mixed environments: pair WireGuard with a fallback in scenarios where dynamic path selection or feature parity matters.
2. IKEv2: steady performance with roaming elegance
IKEv2 delivers reliability when devices drift between networks. It sticks to the same security posture across Wi‑Fi, cellular, and shared laptops, which matters more than raw peak speed in real-world use. If you value seamless transitions and stable connections on mobile hardware, IKEv2 is the protocol that keeps your session from dropping mid‑handoff. How WireGuard vs OpenVPN speed compares in 2026
Why IKEv2 holds up under roaming
Posture: IKEv2’s design favors devices that move. When a laptop wakes on a new network, the tunnel re-establishes quickly, usually without user intervention. This roaming elegance translates to fewer reconnects in transit, a feature privacy‑mocused teams notice in practice. Industry reports point to IKEv2 as a go‑to for corporate mobile clients because the handshake is compact and resilient in variable network conditions.
On multicore devices, IKEv2 often shows strong throughput and steady latency. The protocol’s efficient state management and streamlined cryptographic handshakes make it a practical choice for modern laptops with multiple logical cores. In environments where endpoints run two or more simultaneous VPN sessions, the efficiency gains compound, reducing battery drain and keeping the user experience smooth.
Real-world deployment notes for corporate mobile clients
For organizations managing mobile fleets, IKEv2 is frequently favored because of predictable behavior across iOS, Android, and Windows endpoints. The vendor ecosystem supports native clients with well‑documented roaming policies, allowing administrators to configure persistent sessions that resist network quirks. In practice, this reduces support tickets related to dropped connections during commute or field work, a quiet productivity win.
From a security stance, IKEv2’s core strength lies in how it negotiates and refreshes keys during roaming. The protocol uses EAP for extensible authentication in modern deployments, and it leverages robust cryptographic suites that align with typical enterprise baselines. What the spec sheets actually say is that IKEv2 offers strong mutual authentication and quick rekeying, which matters when users reconnect across networks with varying trust levels.
Subsections
Why IKEv2 shines under real-world roaming
ROAMING COMPATIBILITY matters. The handshake geometry is optimized for quick re‑establishment as networks shift. This minimizes user-visible disruption during hallway transitions between office and café networks or carrier networks on mobile devices.
Performance on multicore devices
MULTICORE EFFECTS accumulate. With parallel processing, IKEv2’s key exchange and child SA handling scale efficiently, yielding steadier throughput on laptops and desktops that juggle multiple VPN sessions or concurrent network tasks.
Corporate mobile client patterns
VENDOR ecosystems reflect a preference for IKEv2 in enterprise mobile deployments. Native clients, policy templates, and centralized key management align with corporate security postures, making rollout and maintenance more predictable.
For roaming-heavy use cases, IKEv2 often delivers the most stable experience without specialized tuning. In practice, that stability matters as much as speed when workers switch networks on the fly.
Notes from the literature consistently flag IKEv2 as a reliable default in mobile‑first enterprises. When you read through vendor guides and changelogs, the recurring theme is stability first, speed second, and roaming support as a built‑in strength. If your environment includes frequent network switches and corporate mobile clients, IKEv2 is the rational default.
3. OpenVPN: reliability with slower baseline
OpenVPN sits in the middle of the speed vs. security spectrum. It is mature, configurable, and surprisingly predictable once you tune the knobs. For environments that must pass through legacy hardware or strict firewalls, OpenVPN remains a reliable workhorse. The catch: you pay in baseline speed. You can wring more performance out of it, but you’ll need careful setup and discipline.
I dug into the documentation and cross-referenced reviews to separate hype from reality. OpenVPN’s core strength is its configurability. You can tailor cipher suites, key exchange, and journeying modes to fit old devices or network ACLs. That same configurability is what trips teams if they treat it as a one-size-fits-all solution. The simplest defaults tend toward stability over raw throughput. When you want speed, you don’t just push a single lever, you rework the entire stack from crypto to transport mode.
Why this still matters in practice
- Mature and configurable. OpenVPN has decades of field use. The codebase is battle-tested, and the community is large enough to surface fixes quickly. If you’re dealing with custom hardware, you’ll find more documented knobs and fallback paths here than in newer protocols.
- Worth considering on legacy hardware or strict firewall environments. In enterprises with older routers or draconian egress policies, OpenVPN’s polyglot support for UDP and TCP transport, plus flexible port choices, helps you slip through hurdles that natively faster protocols stumble over.
- Can be tuned for speed, but gains require careful setup. The naive “enable VPN and go” approach will yield disappointing numbers. Real speed requires aligning cipher choices, TLS parameters, and tunnel modes to the actual network, often in concert with server-side settings and client-side routing rules.
Two concrete knobs to consider
- Transport and mode. OpenVPN offers UDP or TCP transport and a choice of tun/tap devices. If your path includes NAT-heavy networks, UDP often wins. If reliability through flaky links matters more, TCP can reduce packet loss perception. The impact of this choice is real, not theoretical.
- Cipher suite and TLS settings. You can trade message-level security for throughput by selecting lighter cipher suites and tweaking TLS renegotiation intervals. But you’ll want to stay within acceptable security bounds for your threat model. Small changes here compound quickly across users.
What the real-world trade-offs look like
- Legacy hardware. Expect about 20–40% lower peak throughput vs. modern speed champions when you keep legacy CPUs in the loop. The exact delta depends on CPU crypto acceleration and the chosen cipher.
- Strict firewalls. You’ll appreciate OpenVPN’s ability to run over common ports and its resilience to aggressive rules. If your firewall treats nonstandard VPN fingerprints harshly, you may need to standardize on conventional ports and TLS footprints.
Bottom line: OpenVPN is reliability with a slower baseline. It shines where security, compliance, and compatibility trump pure speed. Plan for a measured, incremental tuning process, and you’ll unlock a surprisingly usable throughput profile without sacrificing core protections.
Why OpenVPN holds up under restricted environments
- Compatibility with older hardware and opaque firewalls remains strong.
- Proven stability across a wide range of OSes and devices.
- Predictable behavior once you align transport, ciphers, and TLS settings.
Bottom line: OpenVPN is the dependable choice when legacy constraints and strict networks demand a proven, configurable tunnel that you tune for speed rather than chasing raw throughput.**
4. Lightpath-like or custom TLS-based variants
When speed is the goal, TLS-based variants that skim the wire can feel like magic. The catch is that the performance you see hinges on the cipher suites chosen and how aggressively the stack is tuned. Vendors that push TLS-1.3 optimized stacks often tout lower latency and higher throughput, but those gains aren’t universal. I looked at vendor docs and release notes across several providers, and the pattern is clear: the fastest path in one environment can underwhelm in another unless you align hardware acceleration, cipher selection, and offload support.
A quick snapshot from recent practice shows that cipher choice dominates. If a stack prefers X25519 for the handshake and chooses AES-GCM or ChaCha20-Poly1305 with hardware acceleration, you can shave meaningful milliseconds off the initial connect and sustained throughput under load. But swap in a heavier AEAD like AES-256-GCM on a device without acceleration, and the same TLS variant loses the edge. In other words, speed is a feature of the entire chain, not a single knob.
The practical takeaway is simple: check the vendor docs for hardware offloads and acceleration capabilities. Some vendors expose explicit support flags for AES-NI or dedicated crypto engines. Without that, TLS performance can drift toward the middle of the pack even if the protocol itself is fast on paper. And yes, you should verify that your hardware, CPU, NIC, and any VPN-specific offload cards, is actually leveraging those optimizations. If not, speed gains evaporate when you push concurrent connections.
To ground this in real-world usage, here is a quick decision guide.
| Criterion | Look for in vendor docs | What it means for speed | When to walk away |
|---|---|---|---|
| TLS version and suites | TLS 1.3 with modern AEAD ciphers | Lower handshake latency and higher per-connection throughput | If you see fallback to TLS 1.2 or legacy suites, speed wins are unreliable |
| Hardware acceleration | Offload flags for AES-NI, crypto offload engines | Real, measurable throughput lift under load | No offload support equals weaker scaling |
| Deployment mode | Software stack with optional NIC offloads | Helps sustain peak rates during bursts | Pure software path under heavy concurrency |
Most TLS-based variants deliver real speed only when the cipher suite and hardware offloads align with the workload. Without acceleration, the headline gains crumble under load.
H3 subsections
Why TLS-1.3 optimization matters for speed
TLS-1.3 reduces handshake rounds and removes many legacy fallbacks, which cuts connection setup time in half in favorable conditions. I scanned release notes and vendor whitepapers, and the takeaway is consistent: TLS-1.3 with modern ciphers unlocks the lowest latencies when hardware acceleration is present. If you’re evaluating a TLS-based path, confirm that your environment uses TLS-1.3 end-to-end and that the chosen cipher suite is supported by your crypto hardware. This is where speed becomes predictable rather than aspirational.
Cipher-suites and optimization level
Cipher choice isn’t cosmetic. AES-128-GCM or ChaCha20-Poly1305 with proper microarchitecture support tends to outperform heavier suites on commodity gear. Some stacks offer configurable optimization levels, low, balanced, or aggressive. In practice, “aggressive” wins speed on a quiet network, but it can backfire on noisy links or devices with limited CPU headroom. If your use case includes mobile clients or remote workers on variable connections, test under realistic jitter conditions to see which setting holds up.
Hardware acceleration and vendor claims
Not all TLS stacks benefit from the same accelerators. Some vendors clearly document AES-NI or dedicated crypto offloads. Others leave it ambiguous. The difference is not theoretical. When acceleration is used, you’ll see a clean uplift in sustained throughput and a steadier line during bursts. If the vendor doesn’t publish acceleration support, you should treat any claimed speed gains with skepticism.
Verdict: pick TLS-based variants only if the vendor clearly advertises hardware acceleration, TLS-1.3 readiness, and favorable cipher suites. Otherwise you’re paying for fast marketing, not fast performance.
What you’ll do next
- Inspect product documentation for TLS-1.3 support status and recommended cipher suites.
- Verify hardware offload capabilities on your servers and NICs. Look for explicit enablement flags and firmware requirements.
- Run a sanity test at scale in your own environment, focusing on burst throughput and connection churn, to ensure the promised speed holds.
What to try this week: the concrete moves that move speed and security forward
I looked at eight fast VPN protocols and found a clean pivot: lean into the two that balance speed with solid security for most users. For fast connections with reliable privacy, WireGuard continues to outperform in raw throughput, while OpenVPN remains the safer fallback where a legacy handshake matters. You can get a meaningful improvement by prioritizing WireGuard on devices that support it, then keeping OpenVPN enabled on platforms where interoperability trumps raw pace.
From what I found, the bigger pattern is this: speed alone fails without predictable latency and robust cryptography. The next moves are not exotic configurations but deliberate defaults. Enable the WireGuard profile by default on your home router and laptops, and maintain a backup OpenVPN profile for stubborn networks. If you only do one thing this month, that swap will punch above its weight.
Backup strategy
- Try WireGuard on a modern device first for everyday browsing and streaming. Pair with OpenVPN on networks that misbehave.
- Verify your firewall rules allow the WireGuard port. Keep a documented fallback plan in case a site blocks it.
- Note the date of your last protocol update and re-check the changelog monthly to catch a security-improving tweak.
Frequently asked questions
Does bypassing VPN protocol speed depend on device type
The speed impact of bypassing a VPN protocol depends heavily on device horsepower and network stack maturity. I looked at how different platforms implement the protocol in kernel space vs user space and how they handle cryptography offload. On mobile devices, Rust implementations and tight kernel integration tend to reduce latency and CPU usage compared to older userspace paths. Desktop variants often benefit from multi‑threading and SIMD acceleration. In practice, you’ll see WireGuard often outperform OpenVPN on modern devices, while IKEv2 can hold steady on roaming scenarios. Yes, device choice matters more than you might think when bypassing protocol constraints. Hardware acceleration, OS networking stacks, and the driver support all move the speed needle.
Which VPN protocol uses least battery on mobile
Battery life correlates with CPU load, radio wakeups, and the protocol’s cryptographic operations. WireGuard typically consumes less CPU and wakes the radio less aggressively than OpenVPN, because of its lean code path and minimal handshake. I checked multiple vendor implementations and reviews note WireGuard’s simpler protocol design translates to lower power draw on midrange smartphones. IKEv2 can rival WireGuard in some roaming scenarios but may spike in CPU during frequent reconnects. For long sessions, WireGuard generally wins for battery efficiency. Yes, WireGuard tends to be the most battery-friendly in mobile use cases. Expect OpenVPN to pull more juice during rekeying cycles.
How does WireGuard differ from OpenVPN in speed
WireGuard is built around a small, modern codebase with a fixed set of cryptographic primitives and a concise handshake. OpenVPN uses TLS over UDP/TCP, which adds layers of overhead and more extensive error handling. Real‑world summaries show WireGuard delivering lower handshake latency, higher sustained throughput in comparable networks, and faster reconnects after brief drops. OpenVPN remains robust in complex network conditions and offers broader interoperability, but speed advantages skew toward WireGuard on typical ISP paths and VPN clients. WireGuard is faster in most real‑world paths; OpenVPN is steadier in tricky networks.
Can i mix protocols for different apps
Yes, you can assign different apps to different protocols on many VPN clients, giving you speed for light tasks and robustness where needed. The practice hinges on split tunneling rules and per‑app routing, plus the client’s policy engine. WireGuard may be favored for bandwidth‑sensitive apps, while IKEv2 or OpenVPN can ride through firewalls or captive portals more reliably. Some providers disable per‑app protocol choice in consumer plans, so check the client’s features before you commit. Yes, you can mix protocols across apps where the client supports per‑app routing. This is not universal, so verify vendor documentation.
What cipher suites influence VPN speed the most
Cipher choice matters, but the biggest speed levers are the protocol’s baseline design and handshake frequency. For WireGuard, the cipher suite is fixed out of the box, which minimizes negotiation overhead. OpenVPN’s TLS stack lets you pick ciphers. Modern schemes like ChaCha20-Poly1305 or AES‑GCM deliver strong performance, but switching to heavier suites can add CPU load and latency. In practical terms, the speed delta from cipher choice is smaller than the delta from protocol architecture and network path. The cipher suite matters, but not as much as the protocol’s design.
Do VPNs throttle speed by location
Some providers throttle or shape traffic by region, especially under heavy load or in jurisdictions with strict routing. I looked at vendor policy pages and changelogs where throttling appears as congestion management rather than explicit caps. In practice, you’ll see consistent speeds in regions with dense server fleets and solid peering, while distant or saturated locations slow down. If you’re planning a trip or moving to a new region, run a quick sanity check on your typical destinations and test at off-peak hours. Yes, location can influence observed speed due to routing and congestion management. Look for providers with wide, well‑peered networks and many regional options.
How to test VPN speed without a server near you
Test without a nearby server by measuring tunnel latency to multiple distant endpoints and analyzing peak throughput to those endpoints. Use a lightweight speed test inside the VPN tunnel: ping the gateway, then run a sustained upload/download to a public speed test endpoint, ideally in a region with good peering. Compare results across protocols within the same client to isolate protocol impact. Record at least three runs per configuration and note time of day. Do a multi-endpoint test, then compare across protocols. The process reveals whether distance or protocol is the dominant bottleneck.