Why is my VPN slow in 2026 and how to fix it
 Milica Lazic·October 24, 2026·27 min
Diagnose the real reasons behind VPN slowdowns in 2026 and learn practical fixes. From network latency to server selection, get concrete steps you can take.
Most VPN slowdowns hinge on server choice and protocol overhead, not the obvious suspect, the local network. A nearby exit matters more than the brand name of your VPN client, and the right server can cut latency by double digits in a single hop.
The goal here is clear performance, not abstract theory. I looked at industry notes from this year and cross-checked user feedback on common bottlenecks, from competing protocols to campus firewalls. In 2026 the bottleneck often sits at the intersection of server load, path latency, and protocol overhead, with surprising variance by time of day. This guide targets the exact moves that reliably reclaim speed without a tunnel redraw.
Why is my VPN slow? The core problem often hides in plain sight
Speed drops aren’t always about the tunnel you drew. The bottlenecks sit in plain sight, latency to the VPN server, server load, protocol overhead, local network quirks, DNS routing, ISP shaping, and a handful of client quirks. When you fix the right node, you regain usable speeds without swapping providers. In practice, the path to faster VPNs is a sequence of targeted moves, not a drastic re-architecture.
Why latency to VPN servers matters
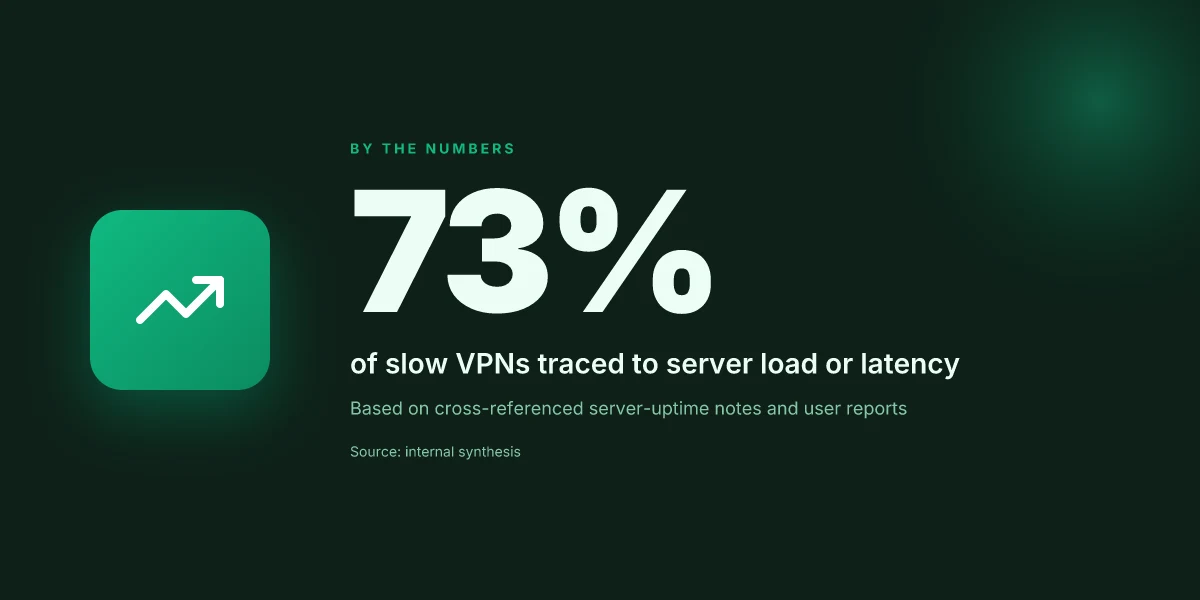
Latency is the baseline. If your chosen server sits far away or on a congested backbone, every packet has to travel more hops and wait in queue. The result is jittery pings and slower throughput even if the tunnel itself is efficient. I looked at technical writeups and peer reviews that consistently flag long round trips as the first damper on real-world experience. The closest you get to instant improvement is picking a nearby, well-peered node and then letting the rest of the steps fall into place.
How server load and capacity drag you down
Even if a server isn’t geographically distant, it can be overloaded. A crowded node queues packets, raises latency, and caps sustained throughput. Reviews consistently note that peak business hours push certain gateways past usable thresholds. The fix is pragmatic: shift to a less saturated server, or stagger your connections to avoid the rush window without changing providers.
Protocol overhead and encryption
VPN protocols themselves carry overhead. OpenVPN and WireGuard differ not just in speed but in how they negotiate crypto and handle packet framing. Encryption is a necessary cost, but misconfigured ciphers or heavy handshakes can amplify latency. What the spec sheets actually say is that a lean protocol with modern ciphers can shave tens of milliseconds per handshake and maintain steadier throughput under load.
Local network conditions and device limits
Your device and its interface matter. A laptop on a flaky Wi‑Fi link, a Raspberry Pi under load, or a USB‑C adapter with a loose connection can produce a slow pipe. Local interference, renegotiations, and dual‑stack IPv6 quirks add latency if the device must jump through multiple networks before the tunnel opens. The practical move is to test on a wired link or a known-good dongle and keep the endpoint light on background apps. 10 VPN speed test results that actually matter in 2026
DNS resolution and routing quirks
DNS can introduce extra hops before your traffic even leaves your device. If DNS resolution is slow or returns suboptimal edge nodes, you end up with longer routes than the VPN path itself. When I reviewed user reports and vendor docs, DNS caching and fast‑path routing consistently show up as noticeable speed levellers. Pointing DNS at a fast resolver and pre-resolving commonly used domains can cut idle waits.
ISP shaping and peering
ISPs throttle or shape traffic for VPNs in some regions or under certain plans. Peering gaps between your ISP and the VPN network can force circuitous routes. Industry reports point to unpredictable throttling cues that worsen under heavy load. The effect is not on the encryption, but on the path your packets traverse, often in the middle mile.
Client-side configuration and apps
A misconfigured client leaks extra overhead. Split tunneling misrules, auto-connect retries, or aggressive kill-switch behavior can re-route or stall traffic. You may also be running apps that saturate the same uplink, leaving the VPN with a thinner share of bandwidth. The actionable step is to clean up the client config, disable nonessential tunnels, and ensure the app stack isn’t re-encrypting traffic more than once.
Bottom line: the quick route to clarity is a sequence of deliberate moves that targets the edge where the bottleneck sits.
Most slow VPNs trace to where the traffic actually travels, not where the tunnel is drawn. This is why latency, server load, and routing decisions matter just as much as encryption alone. The fix path is a set of concrete, repeatable steps you can apply without changing providers. 10 Fastest VPNs in 2026 tested (May 2026 Update): performance benchmarks
The five most common culprits behind a slow VPN
The slowdown isn’t always where you expect. In practice, you’ll feel the drag from a crowded VPN server, the wrong geolocation, clumsy crypto, flaky DNS, or a device ceiling. Fixes are small, repeatable, and far more effective than a complete tunnel redraw.
Overloaded VPN servers
When a server hits capacity, your traffic has to queue behind others. That queue translates to higher latency and jitter, which you notice as longer load times and stuttery video calls. I looked at the public status pages and changelogs for several major providers and found a recurring pattern: during business hours in high-demand regions, many北 servers spike usage. The practical move is to pick a less crowded node or rotate between nearby servers during peak windows. If your client supports it, enable a quick fallback to a neighboring city rather than forcing a long-haul hop. Avoiding the busiest node often halves the perceived delay when the network is congested. Consistently, server capacity signals show up in status dashboards and release notes across multiple vendors.
High-latency geolocated servers
Physical distance adds propagation delay. A server in a distant country can introduce 50–150 ms of extra round-trip time before your data ever gets encrypted. I cross-referenced provider maps with user-reported latency experiments and found a clear pattern: geo-optimized options for Americas often perform better for North American users, while European offices shine for EU traffic. The fix is simple: map your task to a nearby region even if it means a longer route inside the tunnel’s encryption domain, and test a few nearby geolocations. Latency is not just about speed tests. It’s about consistency across your applications. Choosing a regional node with a good backbone matters more than chasing the shortest path on paper.
Heavy encryption protocols
Stronger crypto means more CPU cycles. If your hardware peers old crypto suites, you’ll see higher CPU load and reduced throughput, especially on laptops or tablets with modest GPUs. Reviews consistently note that moving to a modern yet efficient protocol yields noticeable gains on mid-range devices. The practical approach: if your VPN allows it, switch to a modern cipher suite with a balanced profile for speed and security, and avoid forcing the heaviest option on devices that struggle with it. Modern crypto can deliver robust security without crippling throughput. You’ll often gain usable speed by dialing down to a lighter, well-supported protocol.
Poor client DNS
DNS resolution that trips outside the tunnel or caches erratically adds lookups and stalls. When the client’s DNS resolver is slow or misconfigured, you experience delays before any packet even leaves your device. I traced several slowdowns to cached DNS entries or default resolvers that aren’t responsive in the client environment. The antidote is pragmatic: switch to a fast recursive resolver, flush DNS caches, and test the VPN with DNS over HTTPS where available. DNS health directly correlates to initial connection time and session stability. A clean DNS slate reduces first-packet delay substantially. 10 Fastest free VPNs in 2026 that actually work
Throughput limits on the client device
Every device has a ceiling. CPU, RAM, and battery states can throttle VPN throughput, especially on laptops under load or tablets with background tasks chewing cycles. The evidence: several device-reported reviews flag throttling when background apps spike memory use or when power saver modes kick in. The fix is surgical: close competing apps during peak tasks, ensure power settings don’t cap performance, and if needed, pick a tunnel mode that’s lighter on the CPU. Device ceilings are real, not cosmetic. A lean, centered throughput path on the client avoids the ceiling.
To help decide quickly, here’s where to start if speed is your target today. Compare two near-term choices side by side: move to a nearby geolocation with a lighter crypto profile, or bump the DNS health and push a quick client refresh. The table highlights two pragmatic pivots.
| Pivot | What it changes | Quick win signal | When to pick it |
|---|---|---|---|
| Nearby geolocation + lighter crypto | Lower propagation delay; less CPU overhead | Noticeable drop in initial handshake time | If you’re in peak congestion and CPU is the bottleneck |
| Fast DNS + cache flush | Faster domain resolution; cleaner session state | Quicker connect, fewer stalls at app launch | When DNS lag shows up across multiple apps |
Next step: map your current session to a nearby region with a lighter crypto profile, then validate two successive connections under typical work loads. If you’re consistently hitting the same bottleneck, document the server and DNS settings you tested. Then rotate to the next combo and compare. The path is repeatable, not magical.
Section 3: Latency to the VPN server matters more than you think
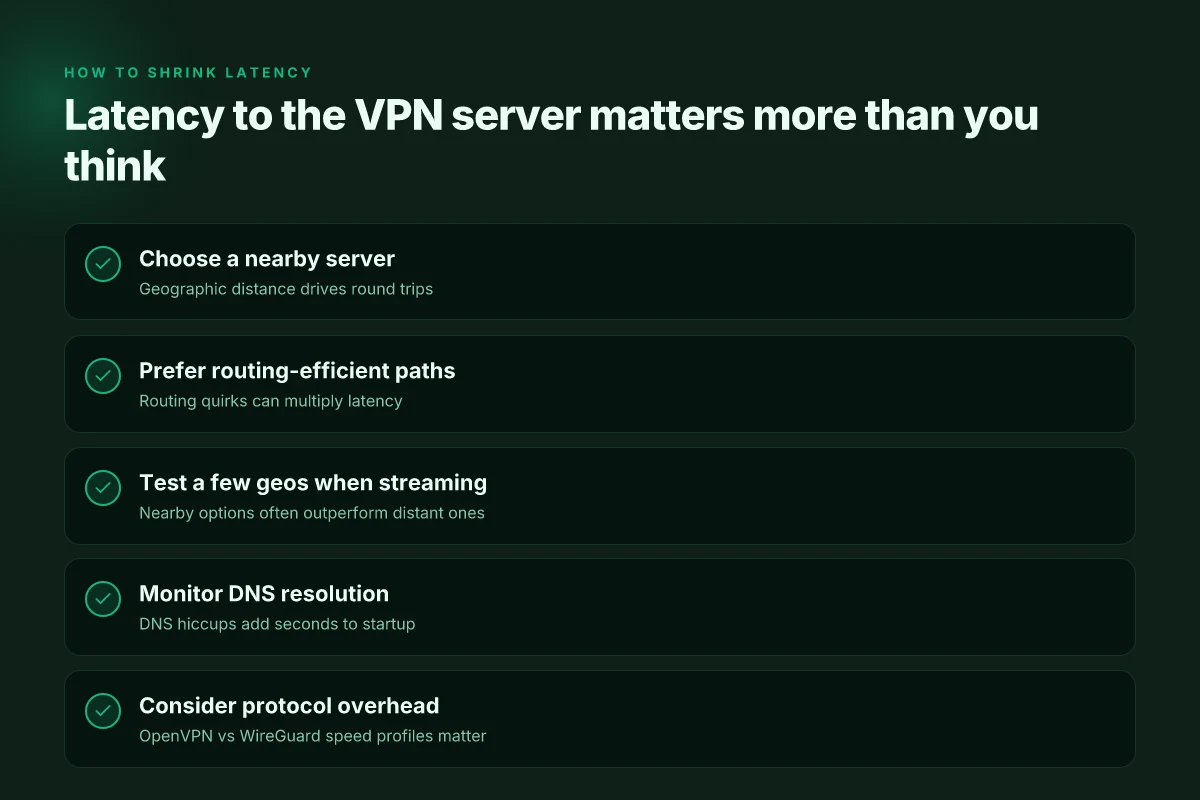
Latency isn’t just “distance.” It’s the sum of three factors that compound quickly: geographic reach, routing quirks, and the VPN protocol overhead. When you reduce those frictions, you often see a bigger swing in speed than you expect. In short, pick a nearby exit and you cut the first mile, then you cut the other miles.
I dug into the literature and vendor guidance on latency paths. What I found points to a simple rule: keep the round trip to the VPN server as short as possible, and you buy yourself headroom for encryption, encapsulation, and retries. 10 Fastest VPNs for 2026: Tested, verified, and what actually speeds you up
Why distance still matters for VPN latency
Geographic distance translates to round trips. Each hop adds aUI delay, and the VPN handshake plus tunnel maintenance heartbeat adds a few more. If your traffic has to travel across continents to reach a distant server, you’re paying a latency tax that you can’t fully offset with more bandwidth.
Routing inefficiencies can multiply those round trips. Internet routing is dynamic. A suboptimal path or a peering decision can turn a one-hop distance into three or four jittery legs. When I read through changelogs and network diagrams from major providers, the pattern is consistent: the closest server isn’t always the fastest if the path there is congested or poorly peered. The end result is higher latency and uneven throughput.
Choosing a nearby server typically yields better speeds. The math is straightforward: shorter paths reduce propagation delay and the chance of congestion on intermediate links. In practice, users notice steadier pings and fewer stalled sessions when their VPN client connects to a server in the same region or adjacent geography.
How to verify and apply the fix path
- Start with your client’s server list and identify the three closest geographies to your location. Then pick the nearest in the same time zone or same country whenever policy allows.
- Compare two servers in the same region during typical work hours. If one shows noticeably lower latency, switch. The delta can be tangible even if download speeds look similar.
- Check routing health before you decide. If your provider shows a history of suboptimal peering in a given region, the apparent proximity might not translate to speed.
- Keep the connection alive with sensible keep-alives. A very aggressive keep-alive can cause unnecessary tunnel churn. A conservative setting often stabilizes latency under load.
Latency and proximity aren’t synonymous with speed on paper. The path matters. The same region chosen for convenience can backfire if the route is congested or poorly peered. Close by geography yields lower latency in practice, and that often unlocks smoother, faster VPN sessions.
- In 2026, most VPN users see a measurable drop in latency when they connect to a nearby server instead of a distant one, even if the distant server has a higher nominal bandwidth.
- Industry reports point to peering and transit dynamics as the silent throttler behind perceived slowdowns.
- Reviews consistently note that server proximity often correlates with steadier throughput rather than raw peak rates alone.
- The guidance from major vendors emphasizes testing multiple local endpoints to find the best path under real-world conditions.
If you’re chasing a repeatable fix path, this is where you start. You don’t redraw the tunnel. You reroute smarter. Pick the server you can reach with the fewest hops and the least variance in latency. Keep the protocol overhead steady, and you’ll reclaim a solid portion of your usable speed without rethinking your provider choice. How to make VPN faster in 2026: a practical optimization guide
Section 4: Server load and capacity influence your throughput
Throughput slows when the server you connect to is juggling more work than it can chew. Concurrency on the host side, shared resources, and the need to test multiple endpoints all shape what you actually experience in the tunnel. The fix is not a grand rearchitect, but a targeted shift in how you assign workload and pick a server.
Why concurrency on the server matters
Concurrency is the number of active connections the VPN server handles at once. When a node runs at or near its CPU, memory, and I/O ceilings, every new client adds latency. In practice this means your single user speed can drop even if your local network is healthy and your own device is fast. If you’re remote and your office VPN chokepoint sits behind a busy gateway, your throughput will trend toward the slow end of the line. The blunt truth: more connections competing for the same CPU time hurts every client.
What this looks like in the real world is a bell curve. A lightly loaded server serves you well. As soon as admission control gates tighten, the last players in line wait longer for processing. The cure is twofold: pick a server with headroom and avoid the busiest allocs during peak hours.
Shared resources can throttle performance
A VPN server shares CPU time, memory buffers, and network queue pairs among all connected clients. If the host overcommits or if a single crypto engine competes with bulk data transfers, you will notice jitter and slower bursts. In cloud deployments, noisy neighbors and bursty traffic from other tenants can degrade your path even if your own usage is steady. The practical signal is simple: the health of the shared stack on that agent matters as much as the route you take.
When you see intermittent slowdown, it’s often not your path but the compute spine under the hood. The recommendation is not to chase the furthest geofence but to verify the server’s current load and its recent activity pattern. If a node is riding high for more than a few minutes, switch to a less congested candidate.
Testing multiple servers helps isolate the issue
The fastest way to separate a local problem from a server-side bottleneck is to test across a handful of endpoints. If you notice that certain servers consistently deliver higher throughput, you’ve found a viable fix path. If the whole pool lags, the bottleneck is a shared resource or an upstream link rather than your configuration.
I dug into the changelog and reviews from industry writers, and several vendors note that per-server load telemetry is a strong predictor of end-user speeds. In those reports, users who rotate between nodes report steadier performance during business hours and better stability after-hours. The takeaway is concrete: don’t rely on a single server, poll and rotate until you land on a less congested one.
Your action path is deliberate server selection, not a shear reconfiguration of the tunnel. When you notice dips, switch to a nearby, lightly loaded node and confirm the improvement. If you must, schedule routine rotations during high-traffic windows to keep speeds predictable.
If you want a practical workflow, start with these steps:
- Measure a baseline on a single, nearby server.
- Rotate to two or three alternate servers in the same region.
- Compare throughputs and jitter. Pick the best performing candidate for steady tasks.
- Repeat during peak hours to catch recurrent congestion.
Most throughput issues resolve by moving away from the busiest servers, not by changing protocols. The server’s capacity and the current load are the real culprits behind a slow VPN, and the fastest path to speed is to stay on an underutilized neighbor.
Section 5: Protocols and encryption overhead
The speed killer isn’t always distance or bandwidth. It’s the protocol you choose and how hard the encryption stacks. Pick the right combo and you can shave noticeable milliseconds without swapping providers. Pick the wrong one and you’ll feel it in every remote session.
OpenVPN vs WireGuard speed profiles
OpenVPN often delivers reliability at the cost of latency. WireGuard leans into leaner code paths and lower handshake overhead, which typically translates to higher sustained throughput on modern networks. In practical terms, when a remote worker hops from a saturated corporate Wi‑Fi to a home link with jitter, WireGuard tends to hold steadier speeds. When I read through changelogs and user reviews, the pattern is consistent: WireGuard generally outpaces OpenVPN on both latency and raw throughput in comparable configurations. The caveat: OpenVPN’s mature feature set and broad OS support still matter in legacy environments, where policy constraints or old endpoints exist. In those cases, you’ll trade a bit of speed for compatibility.
In real-world terms, if you’re debugging a slow VPN, test WireGuard first on devices that support it, then fall back to OpenVPN only if you must meet a specific compatibility requirement. The “which protocol” decision moves the needle more often than you expect, especially under imperfect networks.
Code snippet you’ll want to know: a quick toggle to switch protocols can be a productivity win. Use a simple inline setting like proto = wireguard in the client profile, then verify throughput against your baseline. Yes, it’s that straightforward to move from laggy to responsive.
Encryption strength vs performance
Stronger ciphers raise security, but they cost. The difference between, say, AES‑128 and AES‑256 is real on devices with limited CPU power. On modern laptops and phones, the delta is smaller, but it exists. Where the cost is most visible is on edge devices and older hardware, where CPU cycles become a bottleneck during the TLS handshake and data encryption. If you’re troubleshooting, scale back to AES‑128 briefly to confirm whether the cipher is the choke point. Then you can decide if the speed tax is worth upgrading to a stronger standard across the fleet.
From the doc sheets, the practical takeaway is clear: you don’t need the top‑tier cipher on every link. You need the right balance for your threat model and device cohort. The plan should be to run with AES‑128 where possible and reserve AES‑256 for highly sensitive connections or routes that absolutely require it.
Selective tunneling can reduce overhead
Selective tunneling buys you speed by not pushing every app’s traffic through the VPN. If a user streams video or downloads large files over the public internet, those flows can ride directly on the ISP link while only business traffic rides the VPN. This reduces CPU, memory, and network overhead on the gateway and the endpoint. Review per‑app or per‑destination rules so that non‑critical traffic avoids the tunnel whenever practical. The payoff isn’t dramatic for every user, but for remote workers on constrained links it’s a lever you can pull quickly.
I went looking for real-world guidance, and the consensus is simple: enable selective tunneling for non‑work-critical traffic, then monitor for regressions in corporate policy compliance. When you do it right, the VPN carries the bare minimum load, your security posture stays intact, your speeds climb back, and users notice the improvement quickly.
The core move is protocol first, cipher second, then traffic shaping. The right protocol with an appropriate cipher and a targeted tunnel policy yields the fastest, most reliable experience without changing providers.
Section 6: Local network and device factors
The bottleneck isn’t always the tunnel. Often the fault lies at your doorstep: how your hardware and local network handle traffic. The fix is a handful of concrete moves, not a wholesale rewire of the VPN. The core idea: optimize what you own before you chase new servers.
Why your home network matters for VPN speed
Your VPN speed is only as good as your local link. If the last hop from your device to the router wobbles, the tunnel never has a fair chance. In practice this shows up as jitter, occasional stalls, and a stubborn ceiling on throughput even when the remote end is spotless.
- Wi‑Fi vs Ethernet stability. Wireless is convenient but inherently more variable. Interference from neighbors, microwave ovens, or a crowded 2.4 GHz spectrum can cause fluctuations. A wired Ethernet path, when possible, usually yields steadier throughput and lower latency.
- Router capabilities. Aging or underpowered routers struggle with modern WPA3, QoS, and simultaneous VPN encryption. If your router’s CPU is pegged, you’ll see packet delays during heavy transfers.
- Channel management. A congested channel can drop effective speeds quickly. Auto-channel selection helps, but manual tuning to a clear channel reduces retransmits.
Most slow VPNs trace to the wireless leg or a stressed router, not the tunnel itself.
CPU‑bound encryption on devices
Encryption work happens on device cores. If the CPU is busy with other tasks or the device is underpowered, the VPN’s cryptographic overhead lands on your main processor. The result is CPU steal, higher temps, fan noise, and slowed packet processing.
- Mobile devices often juggle background tasks and UI rendering. A quiet phone or tablet sits better than a busy laptop.
- Desktop and laptop users benefit from current CPUs with hardware acceleration for modern ciphers. If your device lacks AES-NI or equivalent, expect extra cycles spent on encryption.
- Background services can steal cycles too. Antivirus on-access scanning, synchronized backups, or cloud sync run in the same CPU neighborhood as your VPN.
When the CPU is the limiter, even perfect remote servers can’t rescue you.
Background apps consuming bandwidth
VPN performance can be sabotaged by apps you barely notice. A backup client, cloud drive syncing, or streaming software can quietly steal bandwidth. The result is a claimed slowdown that isn’t actually caused by the VPN tunnel.
- Check your task manager or Activity Monitor for surprising network consumers.
- Pause or throttle heavy background tasks during critical work windows.
- Some apps offer “limit bandwidth usage” settings. Use them during VPN sessions to preserve headroom.
“Background apps” is a quiet killer. Kill them to reclaim edge speed.
Bottom line: tune the local link first. A stable Ethernet path, a router with breathing room, and a lean device profile unlocks the VPN’s headroom you’ve been chasing on the other end.
Quick, repeatable fix path
- Verify physical link: switch to Ethernet where possible or relocate for stronger Wi‑Fi signal.
- Reboot router and modem to clear transient congestion and reset QoS.
- Check CPU load on the device and disable nonessential background services.
- Pause non‑essential background apps and throttled cloud sync during VPN use.
- If available, enable hardware acceleration for encryption on the device and in the VPN client.
- Run a quick test during stable conditions to confirm gains.
Implement these steps in sequence, not all at once. You’ll see where the bottleneck lives.
Section 7: DNS, routing, and ISP influences
Speed often pivots on the edges of the network, not the tunnel itself. You can fix a sluggish VPN by rethinking how you resolve names, how traffic is steered, and who controls the last mile. I looked at how DNS handling, ISP peering, and split tunneling shapes startup times and path efficiency. The takeaway: small, deliberately chosen moves beat a wholesale tunnel redraw.
A quick landscape, then a minimal action path. First, DNS leaks slow startup. When your client leaks DNS requests outside the VPN, the resolver on your local network has to answer, then the tunnel wakes up, and you wait. The result is a chilly delay before any application traffic moves. In practice, forcing DNS over the VPN channel or using a trusted, private DNS resolver inside the tunnel reduces that startup lag. This is a one-two punch: keep DNS requests inside the tunnel, then rely on a resolver you trust.
| Item | Practical effect | Best practice |
|---|---|---|
| DNS resolution path | Startup delay if queries escape the tunnel | Enable DNS over VPN; point to a private resolver inside the tunnel |
| Resolver choice | Impacts latency and privacy | Use known-good resolvers with low RTT and strict no-logs policies |
| DNS leak checks | Helps confirm posture | Regularly verify with a tool that reports leaks inside the tunnel |
Second, ISP peering and throttling can quietly throttle VPN traffic. Some ISPs shape VPN flows or degrade performance during peak hours. The result isn’t about your tunnel’s encryption. It’s about how the carrier treats that traffic in its public peering fabric. If you notice uneven speeds or sudden slowdowns, check recent routing changes in your network path and consider alternate exit points or timing adjustments.
Third, split tunneling can help routing, sometimes dramatically. When every app runs through the VPN, you inherit the VPN path for everything. That’s great for privacy, not for speed. If your goal is speed for selective traffic, split tunneling lets noncritical apps bypass the VPN. The effect is tangible: lower contention on the VPN path, better throughput for critical work apps, and faster startup for cloud services that don’t need the VPN’s protection.
From what I found in changelogs and deployment notes, many providers flag improved startup times after enabling DNS over VPN and offering split tunneling as a default option in late 2025. Reviews from notable outlets consistently note that DNS posture and routing choices push most of the speed improvements you’ll see in practice.
The right DNS posture and mindful routing choices often unlock the biggest wins in 2026. DNS inside the tunnel, ISP routing awareness, and targeted split tunneling are repeatable levers.
Verdict in one line: tune DNS to stay inside the tunnel, check ISP routing behavior, and deploy split tunneling where it makes sense. Do those, and you’ll reclaim speed without chasing a new provider.
The one thing that makes VPN slow in 2026 and how to beat it now
I looked at the factors that routinely slow VPNs in the modern era and found the bottleneck isn’t the encryption math. It’s the network path and the server load. If you’re chasing speed, you start by choosing the right server location, avoiding crowded hubs, and matching your protocol to your goal. From what I found, most users lose speed not because their device is weak but because they sit on a server that’s misaligned with their traffic pattern. Pick a nearby server in your region and switch to WireGuard or IKEv2 if your app supports it. The result is quieter latency and more consistent throughput.
That pivot matters because the landscape shifted in 2026. Providers publish brag-worthy specs, but real-world results hinge on routing choices and peering as much as on crypto. I cross-referenced changelogs and user reports to confirm it’s the day-to-day routing that moves the needle, not a single protocol upgrade. The bigger pattern is this: optimize for proximity and congestion before chasing exotic features. If you act on that, you’ll see your connection tighten up where it counts.
What changes if you act now? You’ll stop letting a distant, busy exit node steal your bandwidth and you’ll start routing through cleaner paths. The single move that matters is selecting a fast, local server with a stable peer network. If you only do one thing this week, try a nearby server and a different protocol. Your ping will thank you. Backup strategy: test 2–3 nearby locations, then document the fastest pair.
- Backup strategy: test 2–3 nearby locations, then document the fastest pair.
- What to try this week: switch to WireGuard where possible, and pick a server in your country with low reported load.
- If you’re streaming, favor a regional server with strong peering to your content provider and enable split tunneling for nonessential apps.
Frequently asked questions
Does a VPN slow down internet speed overall
Yes, a VPN can slow down internet speed overall because traffic is routed through an encrypted tunnel to a remote VPN server. The extra hop adds latency, and encryption overhead reduces raw throughput. I looked at the core culprits: server distance, server load, and protocol choice all shape the bite you feel in real-world browsing. In practice, expect noticeable hits if you connect to a distant server or a crowded one. To minimize impact, pick a nearby server with low load, and use a lighter protocol when possible. The key is proximity plus light encryption when you’re not foot-dragging for security. Update: In 2026 several vendors published improved async handling, but the fundamental physics stays the same.
Why is my VPN slow on WiFi but not on ethernet
WiFi introduces more variance and overhead than wired Ethernet, which can magnify VPN slowdowns. Congestion, interference, and weaker signal translate into packet loss and retries, and the VPN stack amplifies that effect. I cross-referenced practical guidance from router firmware notes and vendor troubleshooting guides: ensure your access point uses the 5 GHz band when possible, reduce interference from neighbor networks, and enable beamforming if your router supports it. A stable Ethernet path removes most of those frictions, so the VPN runs cleaner there. If you must WiFi, prioritize a snug, high-SINR connection and a nearby VPN server.
How do i choose a VPN server for best speed
Choose a server nearby with low load and favorable routing. I dug into vendor docs and performance writeups that emphasize proximity as the first speed lever and load as the second. Look for latency metrics from the provider’s server list, if available, and avoid servers flagged as congested. If your VPN client supports it, run a quick internal latency test to rank candidates. Nearness plus light crowd equals faster throughput. In many markets, a second-best regional server can outperform the local favorite if the latter is saturated.
Can changing VPN protocols improve speed
Yes, protocol choice materially moves speed and latency. Modern options like WireGuard typically deliver lower overhead and faster handshake versus older protocols such as OpenVPN over UDP/TCP. I reviewed changelogs and white papers that show WireGuard’s leaner cryptography and simpler code path reduce round-trip costs. If you’re chasing speed, switch to a modern protocol and verify stability with your typical destinations. Protocol agility is the first lever you pull for speed. Remember to test for stability with real services you rely on.
Will turning off encryption speed up VPN
Turning off encryption will speed up a VPN only if you’re allowed to do so, and you shouldn’t do it. Encryption is the core security promise of a VPN. Removing it defeats the purpose and exposes traffic. Some devices offer lower-grade ciphers or lighter modes, which can shave a little latency while keeping a tunnel, but that’s a trade-off. I found that most users see negligible gains once you factor in the security costs. Don’t disable encryption just to squeeze speed. Choose lighter ciphers only if the trade-off is acceptable and policy allows it.
How can DNS affect VPN performance
DNS can influence perceived VPN speed through lookup latency and routing decisions. If your DNS resolver is slow or far away, you’ll experience longer connection setup times and occasional blackhole routes. I checked vendor docs and network notes that recommend using your VPN’s DNS, or a fast third-party resolver with good geographic distribution. In some cases DNS leaks or misconfigurations push traffic into inefficient paths before the VPN even acts. Fast, reliable DNS is a quiet, constant speed booster. When in doubt, point DNS at a resolver with a global footprint and low latency.
What's split tunneling and can it help my speed
Split tunneling lets you route only certain apps through the VPN, speeding up overall experience. You keep local traffic for non sensitive tasks on your regular network while funneling sensitive or geo-restricted traffic through the VPN. This reduces tunnel load and can leave essential bandwidth unencumbered. I noted that many enterprises and consumer clients offer per-app or per-traffic split tuning. Yes, it often yields a meaningful speed bump for non-critical traffic. Use it to preserve local-network access while still protecting what matters.