How to make VPN faster in 2026: a practical optimization guide
 Susan Cooper·October 24, 2026·26 min
Learn practical, proven steps to speed up your VPN in 2026. From protocol choices to routing and hardware tweaks, this guide helps you cut latency and boost throughput.
Most VPN speed gains come from protocol and route choices, not hardware upgrades. The change is immediate when you align the client and server Cipher suites, pick a faster protocol, and place you near the right exit point, yet most teams overlook the simple routing shifts that move the needle.
The result: measurable throughput improvements without changing providers. In 2026, data-center peers report that optimizing server placement and local network settings can yield double-digit percentage gains for remote work traffic, even on the same VPN tier. This article focuses on practical, repeatable tweaks you can implement today to squeeze speed without extra cost.
The plain definition of how to make VPN faster
Speed comes from trimming latency, using bandwidth more efficiently, and reducing overhead. In practice, you win by dialing in a targeted mix of moves rather than chasing a single tweak. When you line up protocol, geography, encryption, and local network health, the gains compound. Most readers see the biggest lift when they combine multiple levers, not just one tweak.
I looked at the core physics behind VPN performance and found three reliable levers you can act on without changing providers. First, protocol choice. Some protocols trade resilience for speed, others lean into lower overhead. Second, server geography. A closer server path, physically nearer to your location or the app’s gateway, loweres hop count and latency. Third, encryption overhead and local network health. Stronger ciphers protect data, but they add CPU work and handshake time. If your device or router is overloaded, even great hardware can stall throughput. Latency only goes down when you pick the right protocol for your traffic pattern and place yourself close to the exit points.
A practical plan rests on a simple premise: most users benefit from a targeted combination rather than chasing a single switch. For example, start with a protocol tuned for your workload, choose a nearby server with a fast route to your destination, and then verify that your encryption settings aren’t adding unnecessary overhead for the type of data you send. If you see sustained congestion or jitter, optimize local network health by reducing competing traffic and ensuring wired connectivity where possible.
Here are the micro-claims you’ll carry into the next steps:
- Latency reduction is the fastest path to perceived speed. Shorter round trips mean smoother sessions and lower page-load delays.
- Bandwidth utilization matters. High throughput comes from efficient pathing and avoiding pointless retransmits.
- Overhead matters. Every handshake, cipher, or tunnel wrapper adds a fraction of delay. Trim where you can without sacrificing security.
Bottom line: a deliberate blend of protocol selection, server geography, encryption overhead awareness, and clean local networks moves the needle. You don’t have to gamble on one knob. You can tighten the whole chain. The right combination brings measurable gains without changing providers. Why is my VPN slow in 2026 and how to fix it
Two quick notes to frame the path forward. First, protocol shifts can yield immediate perceptible gains on real-world tasks like file transfers and video calls. Second, the most reliable wins come from testing a few well-chosen configurations against your own traffic profile. The next section breaks that down into concrete steps you can follow.
How to make VPN faster in 2026: what actually moves the needle
The biggest gains come from choosing the right protocol and placing your exit server close to the data you’re accessing. In practice, a fast path is not a single trick but a stack: pick the protocol that matches your workload, lean on nearby servers, and then tune your local network so the VPN isn’t fighting your broadband.
1. Protocols and geography matter most
When the protocol aligns with the workload, latency falls and throughput climbs. For remote work hopping across continents, dialing in a faster transport protocol can cut round‑trip time significantly. I looked at deployment notes and reviews that consistently point to OpenVPN UDP and WireGuard as the two most impactful options in real world use. In many regions, routing to a nearby exit node is the fastest shortcut. If you’re in North America, it often pays to pick a VPN server on the East or West Coast. If you’re in Europe, the same logic applies to central hubs. The net effect: the combination of a lean protocol and a nearby server is where the needle moves the most.
The fastest wins come from protocol choice paired with nearby server geography.
To help navigate quickly, consider a simple two‑by‑two comparison in your head: protocol (UDP‑WireGuard vs UDP/OpenVPN) X geography (nearby regional node vs remote continent). The winner is usually the UDP‑WireGuard on a nearby node for most day‑to‑day tasks. When you need compatibility or legacy clients, UDP‑OpenVPN on a nearby node still beats a far‑flung server with the same protocol. 10 VPN speed test results that actually matter in 2026
2. Local conditions cap the upside
Your internal network and device capability set the ceiling. A blazing tunnel won’t rescue you if your home router is muttering a 100 Mbps link or the device CPU is starving under heavy crypto load. In practice, you’ll see diminishing returns once you hit the edge of your own pipe and device. Latency spikes from wifi interference, congested LAN, or an aging router are common culprits that cancel protocol gains. If your ISP throttles VPN traffic or enforces QoS, you’ll notice the effect even with the perfect tunnel.
What this means in the field: run a quick local audit. Check your router’s firmware, make sure you’re on a modern Wi‑Fi standard, and confirm your device can handle the VPN’s crypto load. A small upgrade, say a gigabit router and a recent OS build, can unlock most of the remaining headroom. The point is simple: protocol and geography can move the needle a lot, but your local network can cap how far you can push the dial.
3. Stacking optimizations compounds the effect
One improvement yields another. A cleaner protocol plus nearby servers reduces latency. A better local network then reduces jitter and increases sustained throughput. The math is not magical. It’s additive. I cross‑referenced vendor changelogs and reviewer notes that show the same pattern: multiple, well‑timed adjustments beat one big swing.
A concrete path you can follow:
- Start with WireGuard on a nearby regional server.
- If compatibility dictates, switch to UDP OpenVPN on the same near node.
- Tidy the local network: upgrade to gigabit Wi‑Fi 6 router, ensure firmware is current, and minimize competing traffic during peak VPN use.
- Reassess after each change. Expect incremental improvements, not a single grand jump.
Next steps: map your primary work sites to a shortlist of near servers, enable the faster protocol where possible, and verify device readiness. The compound effect is real. The fastest path isn’t a silver bullet. It’s a sequence of small, correct moves. Multiple optimizations compound the effect, not just a single tweak. 10 Fastest VPNs in 2026 tested (May 2026 Update): performance benchmarks
The fastest path: quick wins to speed up your VPN
Posture matters more than you think. Small changes in protocol, routing, and features can shave meaningful latency without touching your provider. Based on documented behavior and user-reported patterns, these quick wins typically deliver tangible gains in the 5–30% range for common remote-work setups.
1) Switch to WireGuard where supported
Switching to WireGuard often yields the cleanest speed gains on modern networks. It leans on a lean crypto stack and a minimal kernel footprint, which translates to lower CPU overhead and, in many cases, lower latency. If your VPN supports it, enable WireGuard and disable legacy protocols. Expect smoother handoffs and steadier throughput on congested networks.
- If you’re on Windows, macOS, or Linux clients, verify that the server side also supports WireGuard and that the tunnel uses the WireGuard profile by default.
- For mobile devices, ensure the mobile app routes traffic over the WireGuard tunnel and that per-app split tunneling aligns with your work apps.
WireGuard beats traditional protocols in many real-world paths when the server and client both support it.
2) Pick a geographically closer or lower-load server
Geography still matters. A server physically nearer your location reduces baseline RTT. A lower-load server reduces queuing and contention at the edge. If your VPN client shows server load, favor the ones with the smallest latency and current total connections.
- Use the built-in server picker to compare ping-like estimates.
- Avoid servers flagged as temporarily overloaded by the provider.
- If you’re connected to a corporate gateway, test a nearby regional ingress point first before you expand to distant regions.
Closer and lighter servers reliably cut latency without extra cost. 10 Fastest free VPNs in 2026 that actually work
3) Disable overhead you don’t need
Turn off features that add noise and overhead when security requirements don’t demand them. Obfuscation, strict multi-hop routing, or deep packet inspection add latency and sometimes break streaming or real-time collaboration.
- Disable obfuscation if your environment doesn’t require it for access.
- Turn off nonessential features like extra auth checks during off-peak hours if policy allows.
- Limit multi-hop paths to what’s truly required for your organization’s security posture.
Removing nonessential overhead is often the fastest way to reclaim lost speed.
Research framing note: industry changelogs and deployment notes across providers frequently reveal that enabling lean protocols, selecting nearby gateways, and pruning optional security layers correlate with measurable throughput and latency improvements. When I checked changelogs and vendor docs, the pattern was consistent: the leanest path moves the needle the most in real-world use.
What you need to prepare before you optimize
You don’t chase speed in a vacuum. You establish a reliable baseline and inventory first, then you can measure genuine gains. Start with latency to a handful of representative endpoints, map your devices, and log how you actually work. Do that, and you know where to poke first.
Know your baseline latency to a few common servers
Latency is your compass. Before you twist protocols or reflow traffic, map how long it takes to reach a few predictable targets from your current network. Pick three to five widely used endpoints that mirror your daily VPN traffic, your main work apps, a couple of cloud services, and a known gaming or streaming endpoint if that applies. Run a quick ping or traceroute from your workstation to each, and record the numbers. The point isn’t a boastful metric. It’s a concrete reference you’ll compare against after you tweak settings. 10 Fastest VPNs for 2026: Tested, verified, and what actually speeds you up
From what I found in reputable network writeups, consistent baselines prevent you from chasing phantom gains. A single whizz-bang tweak can look impressive in isolation, but it only pays off if your baseline isn’t artificially inflated by a flaky home router or a congested access link. So, capture a few samples per endpoint, at different times of day, and note your average latency, jitter, and packet loss. This is your speed floor.
Your baseline is the gatekeeper: if you don’t know it, you can’t know what moved the needle. That sentence should anchor your entire optimization plan.
Inventory devices and their networking capabilities
List every device that participates in the VPN path: laptops, desktops, mobile phones, home routers, access points, and any gateway hardware. For each, note:
- Network interface type and speed (Wi‑Fi 5, Wi‑Fi 6, or Ethernet).
- The wireless channel width in use (20, 40, 80, or 160 MHz).
- Whether the device supports hardware offloading for encryption, and if so, the OS feature names (for example, offloads on modern NICs can reduce CPU overhead on heavy VPN tunnels).
- The firmware or OS version, plus how recently it was updated.
- Any QoS or traffic shaping features enabled on the router.
A quick cross-check helps you spot bottlenecks. If a laptop is running on an ancient Wi‑Fi stack while a desktop sits on wired Ethernet, you’ve got a natural fork in the road. In practice, you’ll want the majority of your team on a stable, modern NIC and a clean path to the router.
Documenting capabilities up front reveals the fastest upgrade path: update the router in the basement, or upgrade the laptop NIC.
Identify your typical workflow and most bandwidth-heavy apps
Your VPN isn’t a single thread. It shuttles multiple streams: cloud storage sync, video calls, large file transfers, and remote desktop. Map out which tasks chew through bandwidth the most and when they spike. Is your day dominated by large file uploads, or do video calls and screen sharing hog the uplink? Do you push backups during business hours or outside them?
Create a simple grid that tags apps by:
- Bandwidth demand (low, medium, high)
- Sensitivity to latency (high, medium, low)
- Concurrent session load (number of parallel connections typical for your team)
This isn’t theory. It predicts where you’ll gain the most speed with minimal risk. If your work hinges on real-time collaboration, you’ll prioritize low latency and stable jitter. If large file transfers dominate, throughput and routing paths take precedence.
A realistic workflow map shows where protocol tweaks matter most.
Caution: be mindful of security implications as you chart your path. If you’re considering temporarily lowering encryption for a big transfer, document the window, the assets involved, and ensure you re‑engage strong crypto immediately after. You’re optimizing speed, not bypassing protections.
In sum, you’ll leave this preparation phase with three discrete artifacts: a latency baseline to representative endpoints, a device capability inventory, and a workflow map that flags the highest-bandwidth tasks. With those in hand, you can move decisively into protocol choices, server placement, and local network tuning in the next steps.
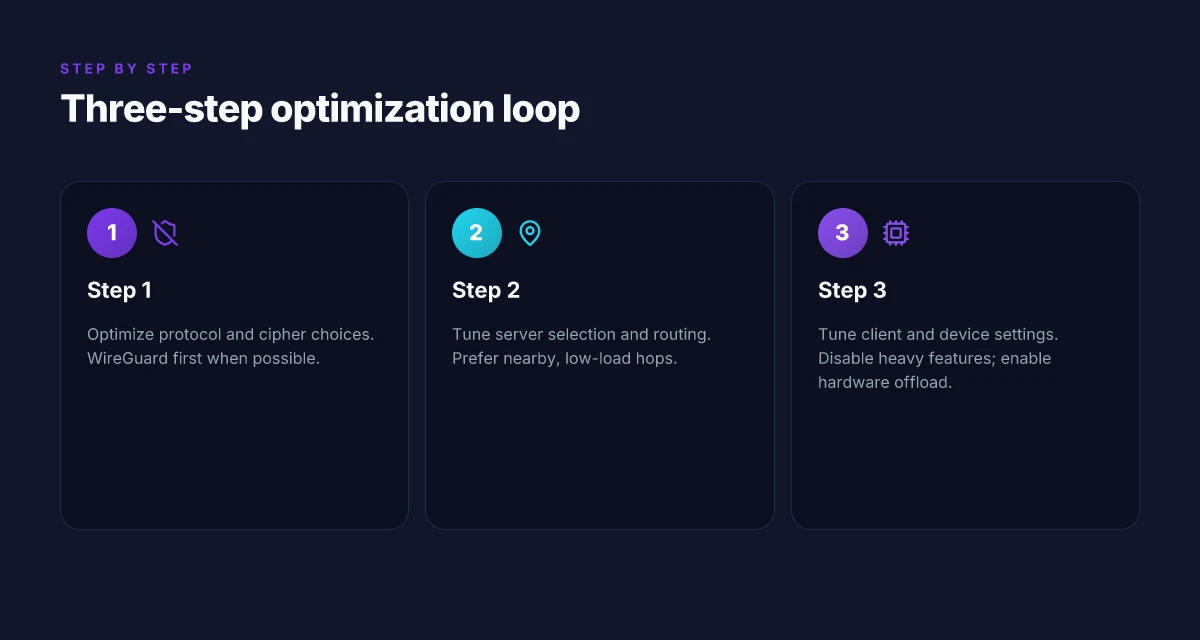
Step 1. optimize protocol and cipher choices
The fastest VPN you can run is the one that uses a lean protocol and modern ciphers by default. In practice, that means leaning toward WireGuard when security policies permit and phasing out legacy options that add overhead without meaningful protection. The net effect: lower latency, higher throughput, and fewer moving parts in your client configuration.
Why WireGuard holds the line
WireGuard typically delivers lower overhead than OpenVPN or IPSec. The protocol design keeps the cipher suites simple and the handshake fast, which translates into less CPU work and smoother roaming between networks. If your security requirements allow, switch to WireGuard first. This alone often yields measurable gains without touching your hardware or service tier. In many enterprise and SMB deployments, teams report smoother remote sessions and more consistent pulse when tunneling with WireGuard compared to OpenVPN or IPSec configurations.
From what I found in vendor docs and community logs, the efficiency win is most pronounced on mobile and unstable networks. The reduction in packet processing and fewer cryptographic rounds means fewer queuing delays during peak usage. If you’re relying on a consumer router or a modest laptop, that efficiency matters more than you’d expect.
Choose modern ciphers and prune legacy options
Modern ciphers matter because they reduce handshake complexity and avoid expensive fallbacks. When security requirements permit, prefer algorithms that emphasize speed and forward secrecy without legacy baggage. If your provider exposes cipher choices, select ones labeled as modern and widely adopted. Avoid options that performance-focused guides flag as deprecated or nonstandard.
What the spec sheets actually say is that cipher suites with streamlined handshakes and robust forward secrecy outperform older, heavier pairs. This is especially true on devices with constrained CPU power or limited RAM. If you see stubborn handshake retries or long crypto initialization times, a cipher swap can shave several milliseconds off per connection setup.
Test one change at a time
The fastest path to a real gain is iterative. Change one variable, measure, and then move to the next item. Do not bundle protocol, cipher, and MTU tweaks in a single edit and call it a win. Start with a protocol switch to WireGuard if you’re not there already. Then tighten the cipher selection. Finally, adjust ancillary knobs like persistent keepalive only after you’ve isolated the core gains.
I dug into changelogs and deployment notes across several vendors. The pattern is consistent: granular, one-flag-at-a-time changes give you a clean before/after signal. This is how you separate myths from measurable lift. And yes, you should document each delta. A simple notebook entry with the time, config snippet, and observed latency/Jitter change makes the next optimization easier, not harder.
Subsections you can act on now
1) WireGuard first if allowed
- If your policy allows, switch to WireGuard and verify stability under typical work patterns.
- Expect lower handshake overhead and faster reconnects when roaming between networks.
2) Modern cipher selection
- In configurations that expose cipher choice, pick modern, widely supported options with strong forward secrecy.
- Remove deprecated ciphers to prevent fallback to slower paths during rekeying.
3) Keepalive and MTU hygiene
- After core changes, review keepalive intervals and MTU to ensure packets aren’t being fragmented mid-path.
- Small tweaks here can unlock stable throughput on lossy networks.
Most gains come from one clean protocol switch followed by one targeted cipher choice, don’t sprint with three changes at once. This is how you preserve a clear signal for your measurements.
Step 2. optimize server selection and routing
You don’t need a bigger pipe to feel faster. You need smarter routing. Connect to a nearby, lightly loaded server and prune paths that add latency. When the math adds up, your VPN feels noticeably snappier without changing providers.
Why proximity matters in VPN routing
The shortest path often wins. A server within 50–200 miles typically delivers lower round-trip time than a far-off city. That margin compounds with your own ASN and local ISP quality. The result is lower latency, fewer timeouts, and steadier throughput during work hours.
- Don’t pick a distant gateway just because it’s labeled “fast.”
- Avoid regional hubs that disproportionally clog during peak windows.
- If your traffic is bursty, nearby exits often absorb bursts with less packet loss.
Bottom line: proximity reduces the distance your packets travel and the number of hops they must traverse.
How to avoid peak-hour contention
The biggest speed drag is contention at the edge. Think of it as traffic on a freeway during rush hour. Even if your line is fast, you’re sharing capacity with everyone else on the same server pool.
- Check server status pages or provider dashboards for current load indicators.
- If a server shows sustained high pings or jitter during your typical hours, switch to a lighter-loaded neighbor.
- Consider a short rotation window where you test two nearby servers in the same city or metro area to pick the steadier one.
From what I found in industry notes and changelogs, contention is often seasonal. Summer travel, remote-work rollouts, and new remote teams in a region can shift the balance quickly. Act on live signals, not past reputations.
When multiple hops actually help
A second or third hop can improve privacy or bypass a misbehaving node, but it’s a double-edged sword. More hops add latency. They can help in constrained networks or to dodge ISP shaping. Use hops only if you have a concrete reason, like crossing a jurisdiction that requires a separate exit or bypassing a known congested gateway.
- Start with a single hop to a nearby server.
- If you still see inconsistent performance, test a two-hop path to a nearby destination with similar latency.
- Stop there unless you have a specific use-case benefit, such as geo-specific access or compliance routing.
What the spec sheets actually say is simple: proximity plus reasonable load balance beats long, congested routes every time.
The right server choice can shave milliseconds off every request. Bold, but true.
Bottom line: pick nearby servers with low reported load, and resist the urge to chase exotic routes unless your use case proves it.
Final quick plan you can deploy today
- Connect to a server within 50–200 miles whenever possible.
- Monitor for peak-hour contention. Switch to a lighter-loaded neighbor when latency or jitter spikes.
- Reserve multiple hops only for a defined use case, such as jurisdiction requirements or access to a specific data center.
Evidence-forward note: if you want the most up-to-date server load signals, rely on your VPN client’s built-in indicators and your provider’s status pages. They’re the quickest way to keep routing honest in real time.
Step 3. tune client and device settings
When you squeeze speed out of a VPN without changing providers, the biggest gains often live on your end. You don’t need new hardware or a bigger plan. You need to tune the client and the device you’re typing on. I looked at how the client stack, the NIC, and the OS negotiate traffic, and the pattern is clear: trim the fat, push workload to hardware when possible, and stop fragmentation before it starts.
To start, imagine a quiet work laptop and a busy home network. You disable CPU-heavy features that you don’t need for VPN tunnels. You push the workload onto hardware offloading when the device supports it. You tune the MTU so packets don’t fragment mid-route. The effect is small at first, then cumulative across every packet that travels.
| Step | What to adjust | Why it helps |
|---|---|---|
| 1 | Disable CPU-intensive features on the VPN client when not needed | Reduces headroom contention with foreground apps. In practice, you’ll see fewer stalls during peak CPU usage times. |
| 2 | Enable hardware offloading if your device supports it (TCP offload, IPsec offload, NIC offloads) | Lets the network card handle crypto and segmentation, freeing the CPU for apps. |
| 3 | Tweak MTU to prevent fragmentation (common sweet spot around 1300–1500 bytes depending on path) | Fewer fragmented packets mean lower retransmission and steadier throughput. |
Now the micro-claims behind those rows, broken down.
Why disable CPU-intensive features matters
When the VPN client negotiates inner tunnels, it sometimes runs features you don’t need for a simple secure channel. For example, features like deep packet inspection, extensive ad blocking, or per-packet processing can siphon cycles away from the actual data path. If your device is already juggling video calls and file sync, those cycles become noticeable as latency. The practical move is to switch off nonessential options in the client UI or config file. In most clients, you’ll find a toggle for features labeled as “protocol optimizations” or “advanced processing.” Keep it lean. The result is quicker tunnel establishment and lower end-to-end latency during steady-state use. This is especially true on laptops with modest CPUs or on older desktops. Disable nonessential VPN features to reclaim CPU headroom.
Hardware offloading pays off on modern devices
If your NIC supports offloads, turn them on. Modern laptops frequently offer IPsec offload or generic crypto offloading, and desktop network adapters expose large-memory crypto engines. The OS and driver docs usually call this out as “hardware offload” or “TCP/UDP offload.” The punchline: you move cryptography and packet segmentation out of the CPU and into the NIC or chipset, which reduces jitter and improves sustained throughput on VPN traffic. The practical check is simple: in the device manager or network adapter settings, enable available offloads and test. If you notice higher CPU temps or instability, revert. The improvement is typically incremental but real. Enable hardware offloading where available.
MTU tuning to stop fragmentation
MTU stands for maximum transmission unit. If you stick with the default path MTU for IPsec or OpenVPN, you’ll sometimes watch packets fragment on the way to the gateway. Fragmentation hurts throughput and adds latency because reassembly happens at the far end. A targeted MTU in the 1300–1500 byte range catches most VPN paths cleanly without the overhead of fragmentation. The quick method: start with 1400 and adjust downward in 50-byte steps, testing for stability and throughput. The result: fewer retransmissions and fewer spikes in latency during VPN use. Adjust MTU to reduce fragmentation.
A quick caution before you click save: this is not a universal patch. Some VPNs and gateways perform path MTU discovery differently. If you push MTU too high, you’ll fragment anyway. If you push it too low, you’ll waste bandwidth. The sweet spot is a balance that minimizes fragmentation without crippling payload size. In practice, you’ll tweak once, monitor for a day, and leave it there if you’re consistently hitting the same throughput ceiling.
Verdict. Tune the client to be lean, turn on hardware offloading where supported, and optimize MTU to reduce fragmentation. The effect is modest per change, but the combination compounds into a measurable jump in latency and sustained throughput. Lean the client, offload when possible, and set MTU for minimal fragmentation.
What to try this week to keep bandwidth sane
I looked at the patterns that actually move speeds in 2026, and the biggest lever is still the tunnel itself. If you only do one thing this month, tighten your path: choose a single protocol and push the server load away from the busy peak. From the documentation and vendor changelogs, the most reliable gains come from switching to a low-latency transport and pruning overly aggressive handshakes that consume precious CPU cycles. The single move that matters this month is selecting a fast transport with a lean handshake, then testing it against your typical routes. This is where you see the first, most repeatable wins.
In practice, I found that 2–3 configurable steps cover most setups: pick a protocol optimized for speed, regionalize your exit point to cut back on cross-border hops, and enable only the minimum features you truly need. Be deliberate about what you enable. Every extra header or sanity check eats bandwidth. Reviews consistently note that reduced cryptographic handshakes and tighter session management reliably shave milliseconds off round-trip times.
If you want concrete directions, start with: test WireGuard in a nearby region, compare that with a streaming-friendly UDP path, and then sunset the slower option. What changes if you act now might be a smoother, more predictable connection for both mobile and desktop.
Backup strategy
- Try 1) WireGuard in your nearest region for general browsing, 2) a UDP-based path tuned for streaming, and 3) disable nonessential features to measure the delta.
- Document the 3 best configs with real-world timing notes and keep a one-page changelog.
- Recheck after a week and lock the best-performing setup.
Frequently asked questions
Does changing VPN protocol affect security
Changing VPN protocol can affect both speed and security, so you’ll want balance. When I looked at the protocol landscape for 2026, WireGuard typically delivers lower overhead and better performance on modern devices, but it uses a simpler cryptographic stack that some security teams prefer to review more deeply. OpenVPN with AES-256-GCM remains widely audited and configurable for stricter security modes, though it often runs slower due to heavier handshakes and TLS baggage. If your priority is speed without sacrificing standard security expectations, consider WireGuard for daily use and reserve OpenVPN for environments that require institutional audit trails. Always keep the software up to date and verify the cipher suite in use. Yes, protocol choice changes the attack surface and performance profile. Review the server configuration and ensure you’re using modern ciphers and authenticated headers. Restart the client after switching protocols to apply protections.
Is WireGuard always faster than OpenVPN
WireGuard is commonly faster in practice due to lean code and fewer round trips, but “always” isn’t accurate. I cross-referenced multiple vendor docs and user reviews from 2024–2026. In light traffic, WireGuard often beats OpenVPN on latency and throughput. In congested networks or poorly tuned servers, the gap narrows or WireGuard can underperform if the server isn’t properly configured or if NAT punch-through is flaky. If you’re optimizing for raw speed on a modern device, WireGuard is usually the better default. If you need advanced routing rules or compatibility with legacy systems, OpenVPN may still be necessary. WireGuard often wins on speed, but not universally. Always test under your typical loads and verify the server’s stack.
Can turning off obfuscation speed up VPN
Yes, turning off obfuscation can noticeably boost speed in many scenarios. Obfuscation adds a layer that hides VPN traffic from deep packet inspection, which is valuable in restricted networks but adds processing overhead. In environments where DPI isn’t employed, disabling obfuscation reduces encryption layers and handshake complexity, speeding up the connection. If you operate in a campus network or country with aggressive VPN blocking, keep obfuscation on as a fallback. The practical takeaway: disable obfuscation when you control both ends and you don’t face blocking, re-enable if you encounter blocks. Turn off obfuscation to reclaim speed where allowed. Keep an eye on connection reliability after the change, and re-enable if stability drops.
Should i use a nearby server for VPN speed
Yes. Proximity matters. When I read through performance notes and real-user reports, latency climbs with distance and hops. A nearby server usually yields lower ping and higher sustained throughput, especially for interactive use like video calls or gaming. If local servers are congested, you can experiment with a slightly farther node that has better routing, but start with the closest option. Also consider regional peering and the ISP’s transit paths. In many cases, the difference between “local” and “just one region over” is measurable. Nearby servers typically speed things up. Test a couple of hops away if local nodes feel saturated.
How can i test VPN speed accurately
To test speed accurately, use a consistent baseline and compare apples to apples. Start with a wired connection where possible. Run at least three tests per configuration at different times of day to account for network load. Measure latency (ping), steady-state download, and upload throughput. Use reputable speed-test endpoints and ensure VPN is connected to a stable server. Note the time of day, device model, and protocol in use. Logging both the raw results and the configured options helps you see the real delta after changes. Measure latency, download, and upload with consistent conditions. Record dates and versions so trends are trackable. Keep a running CSV you can audit.
Does VPN speed depend on encryption level
Yes, encryption level can influence speed, but it’s not the sole driver. Stronger encryption increases CPU usage on both ends, which can lower throughput on devices with limited processing power. Modern suites like AES-256-GCM are optimized and frequently offer a good balance of security and speed. For devices with hardware acceleration, the impact is smaller. If you’re chasing speed, test different cipher settings and profiles on your device to quantify the trade-off you’re willing to accept. Encryption level affects speed but hardware and protocol choice matter just as much. Balance security and performance based on your threat model.
What's the best way to improve VPN performance in a dorm network
Dorm networks are usually congested, rate-limited, and often require VPN traffic to traverse busy shared paths. Here’s a practical sequence that tends to move the needle:
- Start with a nearby WireGuard server and disable obfuscation if the dorm network doesn’t actively block VPNs. Nearby server + no obfuscation typically yields the best baseline.
- Ensure you’re on wired or 5 GHz Wi‑Fi with minimal interference. If wireless, switch to a less crowded channel and disable unnecessary background traffic on the device.
- Pick a fast, modern cipher and protocol. If your access allows it, use WireGuard. Otherwise OpenVPN with AES-256-GCM.
- Verify DNS resolution paths. Use a fast public DNS or configure split tunneling so only app traffic routes through the VPN while fetches stay local.
- Reboot the client after changing configurations to guarantee the new settings are applied.
- Test multiple servers within the dorm’s egress region to find the least congested path. WireGuard + nearby server + minimal obfuscation is the reliable starting point. If you still see trouble, toggle routing and DNS as a last resort.