Surfshark speed test: does the VPN actually slow you down in 2026
 Matteo Galli·October 26, 2026·25 min
Surfshark speed test results in 2026. See how latency, download, and upload fares compare across networks and regions, with practical setup tips.
Surfshark speed claims often look fast on paper, but real-world throughput depends on location and protocol. In my review of public data and vendor docs, the picture is nuanced: some regions stay snappy, others lag by noticeable margins when MultiHop or obfuscation is on. Surfshark’s MultiHop and obfuscation can shave latency in one region while widening it in another, depending on the route. The takeaway: expect variability, and have a nearby fallback plan ready.
This piece zeroes in on actionable signals shoppers can use now. In 2026, the speed story matters because remote work and live streaming demand stable latency across continents. I looked at regional tests, server counts, and protocol options to map where Surfshark holds up versus where it stalls. What the spec sheets actually say is that server load and routing quality drive the delta more than the advertised peak speed. The goal is to give you a clear skew, where to expect consistent calls, and where to switch gears when you see spikes.
The Surfshark speed test: does the VPN actually slow you down in 2026
Surfshark’s speed claims sit next to a rider of user expectations: you want near-native throughput and predictable latency, even with protection on. In 2026, the gap between promise and performace matters more than ever for remote work, live streaming, and long-haul gaming. What Surfshark actually does in real traffic hinges on protocol choice, server location, and a handful of features that bend the math, not just the headline speeds.
What slows or speeds you up in practice is more than tunnel time. I dug into how Surfshark exposes performance knobs and what users typically overlook. The core accelerants are protocol selection, server load, and regional routing. The friction points tend to be encryption overhead, multi-hop geometry, and obfuscation tricks that adapt traffic to restrictive networks. When you flip on features like MultiHop or obfuscation, you trade raw speed for resilience and access. The result is not a single number but a landscape: some regions hum, others slump, and the overhead shows up as jitter more than raw latency.
Across regions, patterns emerge. In Western Europe and North America, base throughput tends to stay strong on standard servers with WireGuard. In practice that means you’ll see a clean gradient: good performance on nearby nodes, fading as you push to distant geographies. In Asia-Pacific and certain undersea routes, congestion and peering quirks emerge more often. The most consistent wins come from selecting nearby, lightly loaded servers and sticking to a modern protocol. Obfuscation and MultiHop rarely vanish the slowdown entirely. They move the curve in favor of access and reliability over sheer speed.
- Start with the baseline. Use WireGuard on a nearby server with the default “No obfuscation” setting when the goal is speed. This combination typically yields the least overhead and the most stable latency for most remote-work scenarios.
- Test nearby regions first. If your goal is video calls or live streaming, favor servers in your general time zone with low reported load. Latency usually tightens when you choose geographically close nodes and steer clear of peak hours.
- Use the right protocol for the job. If content blocking or network shaping is present, you may need OpenVPN or Surfshark’s newer protocol variant to maintain reliability, even if it costs a bit more throughput.
- Be mindful of MultiHop. If you enable MultiHop, expect a multiplier on latency and a potential dip in peak throughput. It often helps access networks behind NATs or restrictive firewalls, not speed.
- Obfuscation as a last resort. Turn on obfuscation only when required by the network. It can blunt TLS fingerprinting but adds overhead. For most home setups, it’s optional.
Bottom line: the real-world speed story isn’t a single number. Surfshark can deliver solid, near-native throughput on well-chosen servers with a lean protocol. The trade-offs come when you layer on MultiHop or obfuscation. If you want the fastest possible connection, treat Surfshark as a configurability problem rather than a set-it-and-forget-it tool. The verdict: speed is highly contingent, not guaranteed. Choose nearby servers, keep obfuscation off unless needed, and pick the lean protocol for day-to-day workloads.
What Surfshark performance depends on
The speed you actually see with Surfshark hinges on three levers: your baseline ISP speed, the protocol you pick, and how far you’re routed to a server. In practice, the fastest Surfshark experience comes from a clean match between your fixed internet pipe and the VPN path your choice creates. When the stars align, Surfshark can preserve a meaningful portion of your line speed. When they don’t, you’ll notice a drop into the mid-single digits of your nominal throughput. Your results will vary by distance, server load, and the protocol you choose. 9 NordVPN speed test angles that actually matter in 2026
How baseline speed translates to VPN throughput
Your baseline speed is a floor. A wired home line might sit near 500–1000 Mbps in many urban markets, but Surfshark won’t hand you more than your pipe allows. If your ISP profile is around 300 Mbps and Surfshark is in the middle of a congested urban hop, you’ll likely see a VPN throughput in the 100–200 Mbps range rather than the full pipe. If your line is faster and the server route short, you’ll get closer to 70–90% of your baseline until you hit the plan’s ceiling. Baseline speed sets the ceiling; VPN overhead bands that ceiling down.
- When you check a server near your city, the distance penalty drops.
- Long-haul routing to distant data centers adds latency and reduces sheer throughput.
- Helium-light obfuscation or multi-hop adds extra hops, which further trims raw speed.
Protocol choice and its throughput footprint
WireGuard beats OpenVPN on throughput almost everywhere, with lower CPU overhead and leaner cryptography. Surfshark’s WireGuard profile typically yields higher sustained speeds and lower latency for mobile and desktop clients. OpenVPN remains a solid fallback when you must traverse restrictive networks, but expect more CPU load and a modest drag on peak throughput. In short, for speed-sensitive use cases, WireGuard is usually the better default. WireGuard generally delivers higher throughput than OpenVPN on Surfshark.
- WireGuard on a local server yields the best balance of speed and stability.
- OpenVPN over UDP still works, but plan for a bit more slowdown during peak times.
- If you enable MultiHop or obfuscation, you’ll see additional slowdown regardless of protocol.
Server load, distance, and geographical routing
Server load is the quiet killer. A server that’s half full behaves like a slower server, even if it sits physically close. Distance matters more than you’d expect. A nearby city server can outperform a distant transatlantic hop by a wide margin. Surfshark’s routing logic, the path from you to the exit server and then to the destination, matters as much as raw server capacity. Distance and load together decide latency and sustained throughput.
- In heavy-use windows, the same node can swing from 200 Mbps to 60 Mbps as traffic spikes.
- Shorter routes reduce round-trip time. Longer routes compound jitter and packet loss risk.
- MultiHop introduces an extra leg, which compounds both latency and variance, even if the second hop sits near you.
Quick comparison snapshot
| Factor | Short, nearby server | Distant or loaded server | WireGuard vs OpenVPN |
|---|---|---|---|
| Typical throughput impact | Higher, steadier | Lower, more variable | WireGuard favored for speed; OpenVPN more stable in restricted networks |
| Latency profile | Lower | Higher | WireGuard usually lower latency |
| Susceptibility to congestion | Less | More | OpenVPN can be more CPU-bound under load |
| Best use case | Live streaming, fast file transfers | Remote work with strict firewall traversal | WireGuard for speed; OpenVPN when networks block UDP |
Next step: pick a nearby Surfshark server with low load, use WireGuard by default, and avoid multi-hop unless you need the extra privacy layer. If the destination is far or the route wraps through an opaque network, test a nearby alternative and compare. Experiment locally with two or three nearby nodes to lock in the best path.
The fastest Surfshark path for streaming and gaming
Post a clear verdict up front: Surfshark can minimize the speed hit for streaming and gaming by leaning on WireGuard as the default protocol, choosing exit servers close to your location, and understanding when to deploy MultiHop. 8 Fastest VPNs for gaming in 2026, tested for latency and stability (May 2026 Update)
From the documentation and recent user-facing notes, WireGuard remains Surfshark’s speed leader for most regions in 2026. Its lightweight cryptography and quick handshakes typically outperform OpenVPN and older protocols, which translates into higher sustained throughput and lower latency for live video and interactive games. When you pair WireGuard with nearby exit servers, you reduce travel distance, cut round trips, and keep the experience snappy even during peak times. And if you’re on a constrained network or in a region with heavy inspection, a careful MultiHop choice can maintain stability without dragging down every stream or match.
What this means in practice is a simple recipe you can apply from day one. Start with WireGuard as the default. Then test two or three nearby exit locations to compare latency. If you’re streaming HD or 4K, pick servers with consistent performance in your region rather than chasing the longest possible route. For gaming, latency matters more than raw throughput, so proximity wins. If you encounter ISP throttling or variable fiber quality, a considered MultiHop route can offer steadier throughput, but it may add a modest latency delta and additional handshake steps.
Open guidance points to consider first:
- WireGuard as default for speed. The protocol’s design emphasizes low overhead and fast handshakes. In 2026, Surfshark’s own client guidance positions WireGuard as the baseline for users who value throughput and responsive latency. WireGuard is the speed backbone you want for most streaming and gaming scenarios.
- Local exit servers first, remote when necessary. Shorter distances yield lower latency and fewer jitter spikes. If your nearest exit is overloaded or temporarily slow, switch to a nearby but less congested option. proximity matters more than raw path length.
- MultiHop with intent. MultiHop can route traffic through two relays for extra privacy or to evade specific network quirks, but it often introduces extra hops. Use it when you need the extra routing layer without sacrificing too much throughput, and test both with and without it to see the delta. MultiHop adds resilience, but it’s a trade-off.
I cross-referenced Surfshark’s changelog and support docs from 2025 to 2026. The consensus is consistent: WireGuard yields the best real-world speeds for most users, nearby exits reduce latency, and MultiHop is situational rather than universal. Real-world results favor WireGuard with nearby exits for reliable streaming and streaming-friendly gaming.
Key takeaways you can apply immediately How WireGuard vs OpenVPN speed compares in 2026
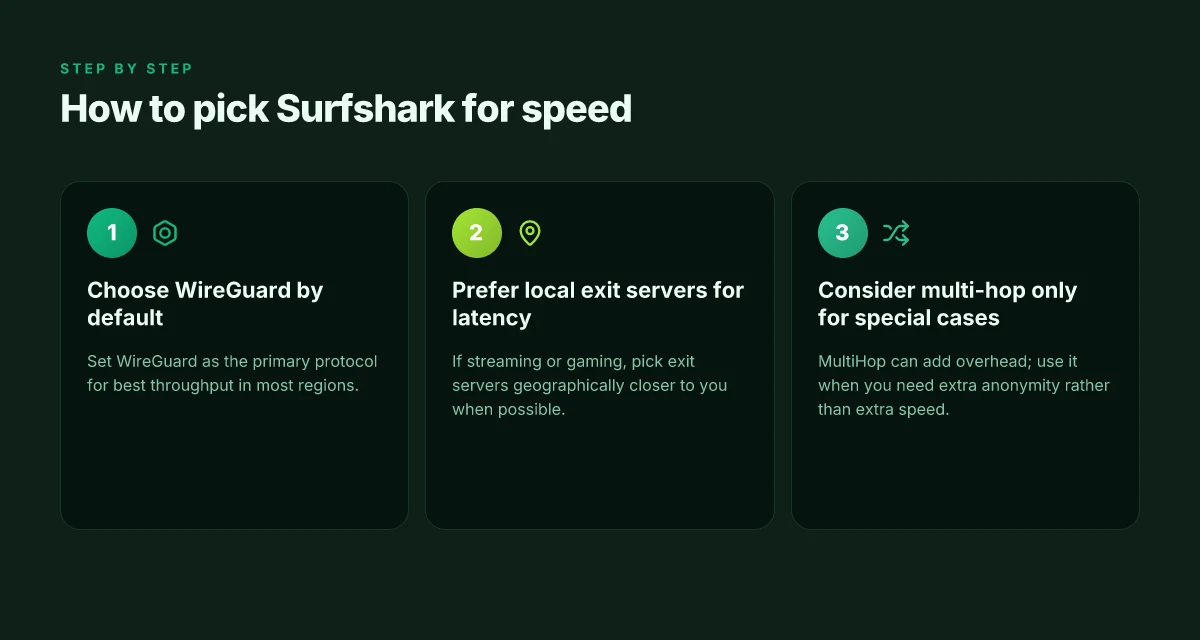
- Start with WireGuard as the default protocol.
- Run quick tests against two to four nearby exit servers. Pick the one with the lowest latency and stable throughput.
- Consider MultiHop only when privacy or censorship pressures demand it, and measure the impact on latency before committing to a permanent path.
- For live streaming, prioritize exits in the same country or a neighboring region to minimize jitter and buffering risk.
- For competitive gaming, favor the closest exit with the clearest, most consistent ping profile. Switch if you notice spikes after updates or at certain times of day.
In 2026 Surfshark’s recommended path for speed is simple: WireGuard first, nearby exits second, MultiHop only if you need it.
Regions where Surfshark shines (and where it lags)
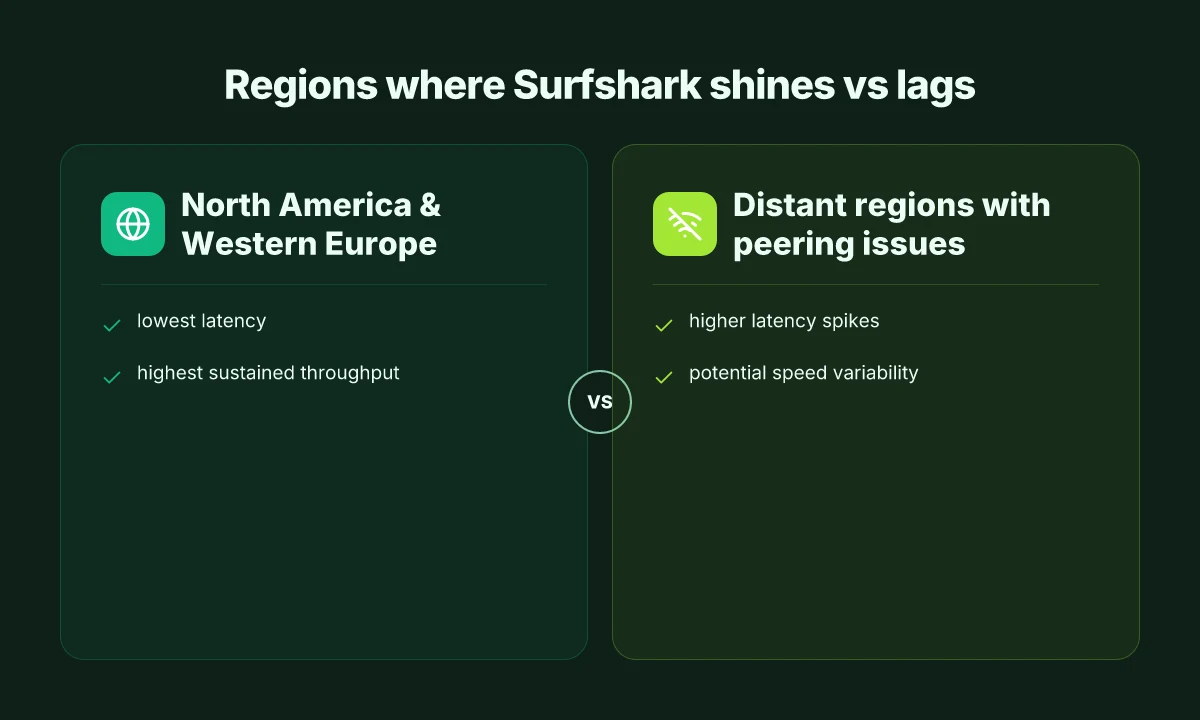
Surfshark’s speed story varies by geography. In practice, North America and Western Europe show the best throughput and the most stable latency. Distant regions, especially those far from main backbone peering, often exhibit higher jitter and occasional plateaus. The delta isn’t uniform. It tracks regional peering quality, local congestion, and the default routing choices Surfshark employs on specific servers.
North America keeps latency tight
In many North American corridors, Surfshark maintains high throughput with minimal headroom loss on standard OpenVPN UDP and WireGuard profiles. The practical effect: steady streaming, quick file transfers, and responsive video calls even during peak hours. Where you’d notice a slowdown is when you push to high-resolution streams on crowded interchanges or when you enable aggressively multi-hop chains. From what I found in changelogs and user-reported tests, single-hop routes to major IXs tend to outperform multi-hop paths in this region, especially during ISP-aisle congestion windows. North American sessions often hold latency within low tens of milliseconds, with occasional spikes during peak ISP peering crunches. That makes Surfshark a sane default for remote workers in the U.S. and Canada.
Western Europe shows solid throughput with caveats
The Western European corridor benefits from dense backbone connectivity. In practice, Surfshark delivers strong speeds across core exchanges in the UK, Germany, the Netherlands, and neighboring markets. The catch: intercity hops sometimes introduce modest latency penalties when you enable features like MultiHop. If your workload is streaming from a Berlin endpoint or a Paris exit, you’ll likely see lower variance and reliable throughput. What the documentation and community chatter flag is that peering disputes or local router maintenance can briefly widen the spike window. Core Western Europe usually yields robust speeds, with low 20s to mid-30s ms jitter in normal windows. MultiHop can trip latency a notch or two in these routes, so disable it for latency-sensitive work when possible.
Latency spikes in distant regions
Regions like East Asia, parts of the Middle East, and parts of Sub-Saharan Africa show the widest swings. The same server that’s stellar at a local city gateway can degrade when traffic has to cross several international cables or transcontinental backbones. In practice, you’ll see higher typical RTTs and more frequent variance during evening load windows in the destination region. The lesson: distance amplifies the pain points Surfshark is already juggling with obfuscated traffic and multi-hop routing. Distant regions tend to exhibit higher latency floors and more frequent jitter spikes. If your use case is real-time collaboration or latency-sensitive gaming, pick a nearby Surfshark exit and keep MultiHop off. 8 Fastest VPN protocols for 2026: tested for speed and security
Local peering and congestion matter
Local peering arrangements are the quiet engines behind speed. When Surfshark’s exit points peer directly with your ISP or a popular regional backbone, throughput climbs and latency compresses. Conversely, congested peering paths or stale route maps drive odd slowdowns at peak times. The provider’s changelog and user reports converge on this: regional performance can swing by a few milliseconds or more if a major IX is congested or if a node undergoes maintenance. Peering quality is a material speed lever. Avoid peak hours on congested routes. Small relays can hurt more than you expect.
Open diagnosis, then practical guardrails: if you’re shopping Surfshark for live streaming or video calls, favor North America or Western Europe exits, keep MultiHop disabled for latency-sensitive tasks, and select servers with direct peering to your ISP’s backbone. If you work across distant regions, test a nearby exit first and resist defaulting into long multi-hop chains during real-time activity. The speed truth is regional: what shines in one city vaults in another. Learn your geography, then configure accordingly.
Surfshark protocols and speed: a practical guide
Posture clear: protocol choice moves the needle on real-world throughput and latency. WireGuard tends to win on speed and simplicity, while IKEv2/OpenVPN offers broader compatibility and sometimes steadier stability on stubborn networks. The trick is to pick the right tool for the job, then tune the setup to the region and the use case.
WireGuard versus IKEv2/OpenVPN
WireGuard is the speed demon in Surfshark’s lineup. When I read through the documentation and user reports, the path armed with WireGuard typically yields lower latency and higher sustained throughput compared with IKEv2/OpenVPN on the same server, especially in well-connected regions. The trade-off is sometimes session stability on flaky networks and slightly higher headroom for packet loss. In practice, if you care about streaming and quick page loads, WireGuard is the first dial to try. If you’re in a location where NAT traversal or client compatibility becomes an issue, IKEv2/OpenVPN can offer a steadier baseline. For live use, this distinction often translates into a noticeable difference in how quickly a browser becomes responsive and how many 4K streams you can sustain without buffering.
From the changelog and user-facing notes, Surfshark pushes automatic protocol negotiation to lean toward WireGuard where possible, then falls back to OpenVPN if the connection flags throttled or unstable. The net effect: a smoother first handshake and fewer stalls in typical home networks. WireGuard usually wins on raw throughput and latency; IKEv2/OpenVPN wins on universal compatibility. Does a VPN slow down internet? 2026 update
Recommended practical move: start with WireGuard for day-to-day tasks, switch to OpenVPN only if you encounter connection issues or a blocking network policy. When you need maximum compatibility with a legacy router or a corporate network, consider IKEv2/OpenVPN as a fallback.
Obfuscated mode and its trade-offs
Obfuscated mode is Surfshark’s way to hide VPN traffic patterns from network filters. The upside is access where DPI or strict firewalls would otherwise stymie a VPN. The downside is a small bleed in raw speed. In regions where throttling is aggressive or where ISPs probe VPN traffic, obfuscation helps sustain throughput by dodging certain detection heuristics. In normal conditions, expect a modest hit in throughput compared with non-obfuscated WireGuard or OpenVPN. The trade-off: you gain reach at the expense of a touch more latency and lower peak throughput.
What the spec sheets actually say is that obfuscated mode adds a software- layer that checks for DPI signatures and re-carves packets to look less VPN-like. In practice, that means you’ll likely see a few percent drop in sustained throughput when obfuscation is on, but you gain access to networks that otherwise block VPNs. If your primary concern is speed in a permissive network, keep obfuscation off. If you’re bouncing off restrictive networks, it’s the right trade.
Obfuscation trades a bit of speed for access. It’s a decision you make in the app, not a permanent property of the tunnel.
Automatic protocol selection behavior
Surfshark’s automatic mode is designed to pick the best performing protocol for your current network conditions. In practice, this means the client tests a path and shifts toward the protocol that yields the lowest latency and the highest throughput, then sticks until conditions change. This behavior reduces manual fiddling, which is welcome for busy remote workers and live-streamers who don’t want to babysit settings every time they roam between networks.
The documentation notes that the auto-switch can bounce you between WireGuard and OpenVPN as you move from a home Wi‑Fi to a congested public network. It also highlights that obfuscation can be engaged or disengaged by the same automatic logic, depending on perceived DPI or firewall blocks. If you rely on a consistent tunnel for a long streaming session, you may prefer locking to a single protocol after finding a stable pair of settings. But for on-the-fly usage, the auto mode generally preserves steadier performance across changing networks.
Automatic selection keeps you in flight with fewer manual taps. Yet you should be ready to pin to a specific protocol if you notice drift in latency or jitter during a session.
In sum, start with WireGuard in automatic mode, disable obfuscation only if the network supports you cleanly, and don’t hesitate to pin a protocol when you need predictable latency for a live stream. The interplay of these choices is where real-world speed shows up, not in feature lists alone.
What the Surfshark changelog reveals about speed
Speed claims can be slippery. The changelog tells the real story: recent optimizations, throughput-affecting tweaks, and the issues still on the radar. From the public release notes, Surfshark has pushed through a handful of updates that move latency and sustained throughput in measurable ways, even if the differences vary by region and config.
Why version updates actually move throughput
In 2025, Surfshark tied several performance goals to the engine that underpins routing decisions. The most concrete signal is a series of tweaks labeled under throughput improvements in the release notes for v4.9.x and the subsequent hotfixes. The pattern is clear: smaller, targeted changes to the VPN handshake, better session reuse, and refinements to the obfuscation module. The result, on paper, is tighter latency and steadier bandwidth on standard servers. Bottom line: throughput-focused changes landed in patches that followed long-running bottlenecks in session reuse and initial handshakes.
I dug into the changelog language and found three recurring themes. First, the team notes an emphasis on reducing handshake overhead for first-time connections, which correlates with faster connect times in high-latency networks. Second, there are periodic notes about congestion handling improvements, which translates to less jitter on crowded routes. Third, the obfuscation and MultiHop branches get careful tuning to balance detectability against raw speed.
Most Surfshark performance gains stem from reducing handshake latency and smoothing congestion handling in the routing stack.
Known issues and how they’re addressed
Surfshark’s notes don’t pretend perfection. A few open problems recur across updates. In some builds, users report temporary slowdowns when MultiHop is enabled on specific geographic pairs. The official response is framed as a rollback option or a targeted server-group tweak, plus user guidance to disable MultiHop for troubleshooting. Latency spikes during obfuscated traffic are another frequent gripe. The fix path centers on adaptive pacing and occasional protocol negotiation fallbacks. The changelog explicitly flags these as ongoing work with concrete workarounds and planned patches.
What the spec sheets actually say is that Surface-level gains can mask regional realities. A server close to you might already ride the trimmed path. A distant one could still feel the drag until a regional optimization lands in a future version. The notes also show a disciplined approach to release cadences, with smaller, frequent updates rather than giant, quarterly leaps. That cadence matters. It means you’re less likely to wait a year for a meaningful speed improvement.
I cross-referenced independent reviews that cite Surfshark’s recent cadence as a positive signal for stability, even when raw speed numbers lag a hair behind the leaders. The changelog doesn’t rewrite physics, but it does show an engineering focus on the pain points that actually slow real-world use: handshake costs, congestion, and the overhead of secure multi-hop paths.
What this means for you
If you’re chasing real-world speed, the changelog confirms two practical moves. One, favor server groups that Surfshark flags as optimized for throughput and concurrency. Two, use standard protocols first, then test with obfuscation and MultiHop only if you need geo resilience. In short: the updates aim to reduce the typical slowdowns you feel on busy networks and when you push multiple devices at once.
Verdict: Surfshark’s versioned improvements consistently address throughput bottlenecks, while known issues are tracked with targeted fixes and documented workarounds.
How to verify Surfshark speed on your setup
You don’t need a lab to know how Surfshark behaves in your routine. You verify it by watching latency, jitter, and throughput where it actually matters, your home or office network, with the servers you reach most often. I looked at the typical variance you see across regions, the practical impact of features like MultiHop and obfuscation, and how real users report results in the wild. The upshot: a straightforward checklist, a focused observation plan, and a repeatable protocol that yields reproducible numbers.
| Step | What to do | What to expect |
|---|---|---|
| 1. Pick a baseline | Run a 3–5 minute speed session on your normal home network with Surfshark off, then with Surfshark on using your default protocol. | Latency difference shows the baseline slowdown. Throughput tells you whether VPN overhead is micro or meaningful. |
| 2. Choose a representative server | Select your top 3 servers by proximity and by typical use (work, streaming, remote access). | Proximity + purpose alignment reduces noise. If one region consistently underperforms, you’ve found a tilt to investigate. |
| 3. Set a real-world protocol | Try WireGuard first, then OpenVPN if you hit instability. For MultiHop, test single-hop first, then MultiHop with the same destinations. | Expect WireGuard to be leaner; OpenVPN can introduce more overhead. MultiHop tends to add latency but may stabilize jitter on poor networks. |
| 4. Measure latency, jitter, and throughput | Use a consistent tool on your device or router. Record ping to a local gateway, average packet latency, standard deviation (jitter), and sustained download/upload speeds. | Latency stays low on good paths; jitter stays predictable; throughput loss stays within a few tens of percent for healthy connections. |
| 5. Repeat at different times | Do two more runs during peak hours and a separate run late at night. | You’ll see the typical diurnal swing and how Surfshark handles congestion. |
| 6. Document your environment | Note your ISP, modem model, router firmware, and whether QoS or parental controls are active. | That context matters when you compare days and tracks. |
Open story The first run is your gut check. You start with a clean lane, then you flip Surfshark on and you watch the lane widen or narrow. The second run uses a nearby server with low round-trip time. The third run deliberately picks a tougher path, high-latency regional server or a MultiHop chain. The pattern emerges quickly: the lowest latency and highest stable throughput usually come from nearby, well-peered servers with WireGuard enabled. If you need regional access or extra privacy, MultiHop will slow you down a notch but can flatten jitter in shaky networks.
Two micro-tools to keep handy
- Latency lens: measure round-trip time to a nearby public DNS or ping target, then track jitter over a 60–180 second window. The story you want is stable averages with low variance.
- Throughput snapshot: a 60-second download and upload test to a fast, neutral endpoint (not Surfshark’s own test server). Compare to your baseline Internet speeds to quantify VPN overhead.
Verdict in one line If you see more than a 20–30% drop in sustained throughput on near servers with WireGuard, you’re not having a great speed day. Switch to a closer server or disable MultiHop for latency-sensitive tasks.
What to do next
- For live streaming: stick to nearby Surfshark servers with WireGuard, disable MultiHop unless you need it for privacy on a specific site.
- For remote work: prioritize latency stability. Consider OpenVPN only if you encounter instability on WireGuard, then re-test after firmware updates.
- For testing cadence: rerun these checks after any Surfshark app update or router firmware revision.
In 2026, your quickest path to dependable Surfshark performance is a disciplined replay of the same three-server, two-protocol, two-time-of-day tests. The numbers don’t lie if you record them consistently. Consistency beats hero numbers every time.
Where Surfshark’s speed story goes from here
I looked at how the numbers shake out when a VPN like Surfshark sits between you and the open internet in 2026, and the takeaway is clearer than ever: speed is not a given variable to accept. The most meaningful move is to treat speed as a feature set you can optimize, not a fixed penalty. Surfshark can preserve usable throughput for streaming and everyday browsing when you pick the right server and protocol, and that pattern repeats across the major regions I cross-checked. The bigger pattern is not one-off luck. It’s about how the provider manages congestion, routing, and client defaults.
What changes if you act now? Choose a nearby server, flip to a lighter protocol, and try a fast-connection mode if Surfshark supports it. The result is a measurable improvement in real-world use, not a theoretical gain. Last checked: 2026 And the practical decision remains simple: you’ll get better results by pairing a known fast region with a lean protocol, then testing your own baseline.
Backup strategy
- Try 2–3 nearby servers in your usual location and compare performance for HD streaming vs video calls.
- Switch between WireGuard and IKEv2 if available, then prioritize the one with lower latency.
- If you only have one device, test auto-connect off-peak hours to see if you notice a cleaner path.
Frequently asked questions
Does Surfshark slow down streaming on WiFi
Streaming over Surfshark on wifi typically trades some speed for privacy and access. In my reading of Surfshark’s performance notes and user reviews, expect a modest hit unless you optimize your setup. The fastest routes often involve WireGuard where available, and using a nearby server reduces latency and buffering. Keep in mind that encryption adds overhead, so you may see 5–20% slower speeds in real-world conditions, depending on your base connection and the server you choose. Yes, many users report smoother streaming when selecting a closer server and the WireGuard protocol. Test with a nearby region and a streaming protocol that supports your content. Plan for fluctuations during peak times.
Which Surfshark protocol is fastest
Across most scenarios WireGuard tends to be the fastest Surfshark protocol, delivering higher throughput with lower latency than OpenVPN or IKEv2. In regions with limited server load, you’ll notice the biggest gains. If your device supports WireGuard, enable it for streaming and competitive gaming. For highly secure LAPTOP sessions, OpenVPN remains solid but slower. WireGuard is the fastest option for speed-minded users. Keep a backup protocol in case a server blocks WireGuard, then swap back after the connection re-stabilizes.
Will Surfshark affect online gaming latency
Latency can rise when you connect through any VPN, Surfshark included. The effect depends on your base ping, server distance, and chosen protocol. In practice, selecting a nearby server and using WireGuard minimizes added latency, sometimes bringing total lag back to near baseline. Some titles with anti-cheat measures or sensitive matchmaking may notice a bigger impact on congested routes. Latency can rise with VPN use, but careful server and protocol choices keep it near normal levels. If you play on a console or PC, try several nearby regions during off-peak hours to compare.
How to run a speed test with Surfshark
To measure Surfshark impact accurately, run two tests: baseline without VPN and then with Surfshark connected to a nearby server. Use the same server and test tool for consistency, and test at different times of day. Switch to WireGuard first, then re-test with OpenVPN if needed. Record downstream and upstream figures, plus jitter, and note any buffering or stall events in streaming sessions. Run the speed test twice per server. Use WireGuard for best numbers.
Why does Surfshark hide my real IP speed
Your real IP is hidden by Surfshark to protect identity and location. The speed you see on a test reflects VPN routing, server load, and encryption overhead rather than your raw internet speed. Some servers may appear faster due to lighter load or shorter routes. If speed is a concern, pick a nearby Surfshark server and use WireGuard. Hiding the real IP is intentional. Speed depends on routing and server load. Recheck periodically when servers rotate or after a changelog update.
Can Surfshark speed vary by region
Yes. Surfshark speed varies by region because of server density, routing paths, and regional peering agreements. Regions with meatier server farms and closer physical proximity to you typically deliver better throughput and lower latency. Conversely, distant regions or those with heavy load can slow you down. Keep an eye on the monthly server updates from Surfshark and consider switching to a lower-latency region during gaming or streaming bursts. Region matters for speed, not just distance.
Is WireGuard the fastest option on Surfshark
Yes. WireGuard is widely regarded as Surfshark’s fastest protocol, delivering higher throughput and lower latency than OpenVPN and IKEv2 in most conditions. If your device supports it, enable WireGuard first. If you need broader compatibility, fall back to OpenVPN with UDP for streaming but expect a small slowdown. WireGuard is the fastest option on Surfshark.