Does a VPN slow down internet? 2026 update
 Susan Cooper·October 25, 2026·25 min
Explore how a VPN can affect internet speed in 2026. I break down the factors, what you can measure, and practical steps to minimize slowdown.
A common misread: VPN speed drops are a feature of the path, not a bug in the encryption. The missing piece is how many hops, which geography, and which protocol you pick. A nearby server with a lean protocol can swing your latency by 20–40 ms and nearly erase buffering during peak hours. Keep the tunnel simple and the path short. That single choice often moves the needle more than a dozen config tweaks.
You’ll see how to quantify impact with a fast baseline, how to spot busy servers, and how to pick routes that align with streaming, gaming, or remote work. In 2026, user-reported speeds cluster around a small set of predictable bottlenecks, not some dumb inevitability of encryption, and that clarity changes the deployment math for teams and individuals alike. Understanding the mechanics lets you act with confidence, not guesswork.
The plain truth: does a VPN slow down internet
Slow is not a default fate. A VPN can tug on latency and shave some bandwidth, but the degree depends on how you route traffic, which server you pick, and which encryption you use. When you line up the factors, speed isn’t a mystery. It’s a function of path choices and configuration.
Choose distance over mystique. The farther your VPN server sits from you, the longer the trip for your packets. It’s basic geometry. If you’re streaming or gaming, aim for a nearby server with enough capacity. A local hop often saves milliseconds that matter for single-digit latency games or smooth 4K streaming. This is where speed is a product of routing hygiene, not magic.
Protocols matter more than you think. Some protocols carry more overhead than others. WireGuard tends to offer lower latency and steadier throughput on many networks, while traditional OpenVPN can be heavier to encrypt and de-encrypt. In practice, selecting a lighter, modern protocol often preserves speed without trading away security. If you’re on a congested network, switch protocols before you switch servers.
Encryption is a lever, not a wall. Stronger ciphers can introduce CPU overhead, especially on older devices. Modern devices handle contemporary ciphers efficiently, but if your device is dated or underpowered, you’ll feel a slowdown before you notice the security gains. The fix is usually not more crypto, but a lighter handshake or a protocol that’s friendlier to your hardware.
Routing is the hidden dial. Your traffic may detour through extra nodes due to server load, peering, or ISP routing quirks. Results vary by time of day and region. I went looking for how providers handle this and found that many maintain multiple exit points to reduce backhaul. That matters more than you’d expect if you’re chasing ultra-low latency. How to make VPN faster in 2026: a practical optimization guide
In practice, a well-chosen server and the right protocol can hold speed steady. You’ll notice fewer slowdowns when you test a nearby, lightly loaded server and a protocol tuned for low overhead. The average user who fixes the basics, server choice, protocol, and client settings, often keeps streaming and gaming within a comfortable margin.
Bottom line: some slowdown is inevitable. But most of the time you can keep it tolerable with concrete checks and a few configuration tweaks. The right server and protocol often preserve speed rather than sacrifice it. Latency falls when you reduce round trips and let modern protocols do the heavy lifting.
H3 Why server choice and protocol hold up under real-world conditions
- Short hops beat long paths. Use a nearby server with capacity to reduce round-trip time.
- WireGuard vs OpenVPN. In many setups, WireGuard delivers lower overhead and steadier throughput.
- CPU cycles matter. On older devices, lighter ciphers avoid noticeable slowdowns.
- Exit points matter. Multiple endpoints reduce backhaul and jitter during peak hours.
H3 What the numbers look like in real deployments
- Latency can rise by a few to tens of milliseconds with distant servers, but nearby options often keep it near your baseline.
- Throughput stays strong on protocols designed for speed when the server isn’t congested.
What I found in the documentation and reviews: speed is not an immutable obstacle. It’s a negotiation between distance, protocol, and device capability. When you optimize those levers, the VPN thread in your internet fabric becomes a lot less conspicuous. Choose a nearby server, pick a lean protocol, and keep encryption anchored to your device’s capabilities. Why is my VPN slow in 2026 and how to fix it
How VPNs affect speed in practical terms
The short answer: speed is a function of path quality, not a VPN’s mystique. You’ll notice higher ping in gaming, potential bitrate dips for streaming, and variability in page-load times depending on where you route traffic. Encryption adds CPU overhead, but modern hardware largely absorbs it. Distance to the VPN server and the number of hops in the path matter more than you expect.
How distance and hops drive the pain
The farther you travel to reach a VPN exit, the more latency you add. That extra handful of milliseconds isn’t just “traffic.” It’s a real cost from each routing hop plus the time it takes for the VPN tunnel to encrypt and forward packets. If you pick a server 6,000 kilometers away, you’re trading potential speed for the privacy or access you want. If your destination requires crossing multiple networks, the packet’s journey compounds delays. In practice, this means two things you’ll feel right away: higher ping cues in fast-paced games and slower initial page loads as routes settle.
To minimize impact, prioritize nearby servers for interactive tasks and reserve distant nodes for tasks that tolerate latency, like bulk downloads or geo-unrestricted browsing. A small but real lever: keep a handful of preferred servers for different activities and switch between them with one click.
Encryption overhead and hardware realities
Encryption isn’t magic. It adds CPU work on both ends, especially with strong ciphers. On consumer hardware, modern CPUs with AES-NI accelerate this. In other words, a laptop or phone with current processors will absorb most of the overhead for typical VPN protocols. The effective hit depends on the cipher and handshake complexity. If you’re on an older device or using an obfuscated or heavier protocol, you’ll notice more friction. The good news: the delta shrinks as devices get faster and vendors optimize defaults.
I dug into changelogs and vendor docs across major clients. What the spec sheets actually say is that the cryptographic load scales with the selected cipher strength and handshake patterns, not with the act of VPN usage itself. When you enable modern defaults and keep the client updated, the overhead becomes a background cost rather than a visible drag. 10 VPN speed test results that actually matter in 2026
Streaming, gaming, and day-to-day web
You may notice streaming bitrate wobble and occasional stalls when routing traffic through a VPN, but this is highly config dependent. For streaming, the bottleneck is often the VPN’s exit bandwidth and the server’s current load. If the exit node is saturated, you’ll see lower sustained bitrates rather than a fixed slowdown. For gaming, the problem is latency more than raw bandwidth. You’ll feel lags as higher ping enters the loop, even if the available bandwidth remains reasonably high. Regular web browsing tends to be least affected, provided you’re not on a congested, distant exit.
To keep things smooth, test a few configurations: switch to a nearby server for low-latency tasks, enable split tunneling where appropriate, and ensure the VPN client uses a protocol that balances speed and security for your use case.
| Item | Near-terms impact | Why it matters | Quick fix |
|---|---|---|---|
| Nearby server | Lower latency | Shorter route reduces ping | Add a local server in your region and default to it for real-time tasks |
| Distant server | Higher latency | More hops and longer encryption path | Use near servers for gaming and daily browsing; reserve far nodes for region-locked content |
| Encryption protocol | CPU load varies | Heavier ciphers cost CPU, lighter ciphers risk security trade-offs | Prefer modern, hardware-accelerated ciphers; update client |
| Exit-node load | Variable bitrate | Shared bandwidth can throttle streaming | Switch off busy nodes; pick ones with lighter load reports |
Most readers will feel speed changes more from routing distance and server load than from any single cipher tweak. Choose servers with proximity and current load in mind, then lock in profiles for tasks like gaming versus streaming.
One concrete next step
Open your VPN client. Create two profiles: one labeled “Near for gaming” and one labeled “Near for streaming.” Set the gaming profile to a nearby country and enable the protocol you know gives the best latency on your device. Set the streaming profile to the same region but with a lightweight cipher where available. Then test a quick latency check for gaming and a short bitrate test for streaming. You’ll likely see the most tangible gains from server choice and protocol defaults, not from chasing a universal speed claim.
Why speed changes when you connect to a VPN
Short answer: routing goes long and tunneling adds overhead. The rest is detail you can actually act on. 10 Fastest VPNs in 2026 tested (May 2026 Update): performance benchmarks
From what I found, two forces dominate the speed dial: geographic routing and tunnel overhead. When you slide into a VPN, your traffic leaves your house route, to the ISP backbone, to a VPN server halfway around the world, then back through another set of networks. Each hop adds latency. The VPN tunnel itself trims or taxes bandwidth depending on the protocol and the CPU work required to encrypt and decrypt. In practice, that means the middle mile, not the last mile from your modem to your ISP router, is where the speed tug-of-war plays out.
Here are the concrete takeaways you can apply today
Geography matters more than you think. If your chosen VPN server sits far from your location, you pay extra round trips. A server 50–100 ms closer can shave meaningful wall-clock time, even if it isn’t the nearest city. Backing this up, industry data from 2024 shows that latency largely tracks physical distance and the number of cross-border hops. The net is simple: pick a nearby exit if you can. That choice often beats any tweak to the client itself.
Tunnel overhead is real but manageable. Every packet traverses an encryption layer, an encapsulation wrapper, and potentially a multi-hop path. The effect compounds when you stream or game, where small jitter matters. The net: don’t expect magic. Expect predictable ceilings and plan around them. Turn on only the required features to reduce CPU work and you reduce the overhead without sacrificing security.
Your ISP still calls the tune for last-mile performance. The VPN can shuffle the middle miles, but it cannot leapfrog a congested local link you rely on each morning. In practice, you’ll notice the VPN’s impact mostly when your last-mile is already stressed or the VPN server is under heavy load. Your ISP still controls the bottleneck, not the VPN provider. 10 Fastest free VPNs in 2026 that actually work
Some protocols are lighter on CPU and bandwidth than others. The choice of protocol changes the balance between speed and security. In broad terms, lighter-weight protocols reduce CPU overhead and can push throughput higher on the same hardware. But they may expose different security trade-offs. The doc sheets and changelogs consistently flag this tension, especially when you push to 4K streaming or ultra-low latency gaming.
I dug into the documentation and release notes across several major VPN ecosystems. The threads are consistent: the speed story isn’t “the VPN is slow” by default. It’s “the path and the proxy math you set up matter more.” If you want to optimize now, target three levers: pick nearby servers, simplify the tunnel configuration, and tune protocol choice for your workload.
Most readers will see the biggest gains by selecting a nearby server and using a lighter protocol when appropriate.
Common slow-down scenarios and quick tests
You can diagnose most slowdowns with two passes: locate the bottleneck, then validate with a quick round of targeted checks. Start near you. Then move outward to nearby exit servers. The objective is to keep latency within your comfort zone for streaming, gaming, or remote work.
Short distance first, then expand
When you connect to a VPN, long-distance servers instantly raise latency. The practical move is to test nearby exit points before you touch distant ones. If a local server delivers solid throughput, you’ve got a baseline. If not, the issue isn’t the protocol, it’s the path. Test nearby exits first to gauge baseline latency and jitter. If your home city shows 15–30 ms better latency than your usual remote server, that’s a signal to pin a local exit for routine work. 8 Fastest VPN protocols for 2026: tested for speed and security
Encryption level and CPU load
Encryption is not a black box. The heavier the crypto, the more CPU cycles you burn. On older devices the effect compounds. If you notice buffering or stuttering during peak hours, drop to a lighter cipher or enable a hardware-accelerated mode if the client supports it. High encryption banks on CPU. Older devices feel this more. A modern laptop or phone often handles typical TLS256 like a champ, while midrange gear can trip over full 256-bit AES at high tunnel throughput.
Free VPNs and crowded planets
Free options lure you with no price but often throttle or crowd servers. You’ll see congestion, variable latency, and reused IPs that bounce across users. If you’re chasing reliable streaming or steady gaming, a paid option is worth it. Free VPNs often throttle or reuse crowded servers. Invest in a reliable paid option. Paid services usually publish performance baselines and give you a wider pool of near locations, which helps keep throughput stable.
Quick tests you can run (no lab gear required)
- Nearby exit ping test: connect to two local exits, run a minute of playback or a quick speed test, compare latency and jitter. If nearby exits outperform distant ones by a noticeable margin, keep the local exit for day-to-day tasks.
- Cipher-suit toggle test: switch from AES-256 to AES-128 or enable hardware acceleration if offered. Recheck throughput and latency. If the difference is material, you’ve found the bottleneck.
- Server density check: rotate to a different country within the same region and watch change in round-trip time. A 20–40 ms swing is typical when servers are crowded. If you see larger swings, steer toward providers who publish steady-state baselines.
Most readers will find speed stability when they stick to nearby exits and avoid overkill encryption on older devices. The soft border between “fast enough” and “too slow” is often a matter of path choice, not magic settings.
If you want a concrete filter: start with two steps. First, lock in a nearby exit with low ping. Second, verify that the device can handle the chosen cipher without stalling. If both hold, you’ve found your fast lane.
Understanding VPN protocols and their speed profiles
Speed is not a given flaw of VPNs. It’s a function of path selection, server load, and the protocol in use. The right protocol, paired with sane config and a nearby exit node, can make streaming feel native and gaming feel responsive. When you pick a path that matches your device and use case, the slowdown shrinks to a bottleneck you can diagnose, not a systemic flaw. How WireGuard vs OpenVPN speed compares in 2026
Why OpenVPN still matters in practice
OpenVPN remains the workhorse for versatility and compatibility. It shines when you need deep configurability and cross-platform support, especially on older hardware or nonstandard networks. But on devices with limited CPU cycles, its crypto overhead can show up as extra latency and jitter. If you’re on a midrange laptop or a budget mobile device, expect the same bottlenecks you’d see from other heavy encryption schemes. On modern gear, OpenVPN can feel very smooth, provided you tune cipher selection and compression with care.
From what I found in vendor docs and user reviews, the trade-off is clear: OpenVPN’s flexibility can cost you cycles. The pace of the tunnel hinges on CPU budget and the chosen cipher. In scenarios where hardware decodes multiple streams simultaneously, the difference between leaner stacks and heavier stacks becomes visible quickly.
WireGuard’s lean design and real-world speed
WireGuard arrives with a leaner code path and a simpler handshake. The design minimizes context switches and cryptographic overhead, which translates to lower per-packet processing on capable devices. For modern laptops, phones, and mid-range routers, that translates to snappier init times and steadier throughput, especially when you’re negotiating with a tight MTU and stable peer stability.
What the changelog and vendor docs emphasize is the same: WireGuard tends to outperform traditional VPN stacks on contemporary hardware, with fewer surprises under fluctuating network conditions. Reviews consistently note smoother initial handshake times and lower CPU load when streaming or syncing large files. If your use case centers on mobile or heterogeneous devices, WireGuard often delivers a cleaner experience without sacrificing security.
IKEv2’s mobile balance and stability
IKEv2 sits in the middle, offering strong stability for mobile networks and decent throughput. It’s particularly effective when you switch between cellular and Wi‑Fi, because it handles roaming events with less disruption than some alternatives. The protocol’s efficiency stems from its streamlined handshake and robust UDP transport, which helps preserve battery life and reduce reconnects in unstable networks.
From the literature, IKEv2 is frequently recommended for remote-work scenarios on phones and tablets. It holds up well under poor signal, maintaining session continuity without a frantic reconnect cycle. If your team relies on mobile access or field devices, this is often the most pragmatic choice.
The quick takeaway: wire the right protocol to the right device. When speed matters, the device’s architecture and the network’s stability often decide more than the VPN choice in isolation. Choose WireGuard for modern hardware, IK Ev2 for roaming mobile contexts, and OpenVPN as a flexible fallback when you need broad compatibility.
Inline reference notes: In 2026, vendor documentation and independent reviews converge on the same pattern. WireGuard delivers the cleanest path on modern devices, IKEv2 excels in roaming mobile contexts, and OpenVPN remains indispensable where configurability and compatibility outrun raw speed.
Where speed actually matters: use-case driven advice
Streaming, gaming, and video calls each ride speed differently. The fixes are concrete, not generic. For streaming, pick a nearby server that speaks your streaming service’s protocol. For gaming, prioritize latency over raw bandwidth and test several servers. For video calls, aim for a stable, consistent connection rather than the highest possible throughput.
Streaming well when distance is the bottleneck
Answer first. Yes, you can keep quality high by routing to a nearby server that supports the service’s protocol.
I dug into how providers pair VPNs with streaming. When you select a server that’s geographically close to the streaming platform you’re watching and ensure the protocol aligns with that platform, you avoid extra hops and transcode overhead that kill picture quality. In practice, users see fewer stalls and sharper 4K clips on popular services when the VPN client lets you pick a nearby exit and a compatible protocol like WireGuard or IKEv2.
- Pick servers within roughly 2,000 miles (3,200 kilometers) of the source. The nearer the exit, the fewer midstream hops.
- Prefer protocols tuned for speed and reliability with streaming traffic, such as WireGuard. If your service blocks that, fall back to a stable IPSec/IKEv2 profile.
- If buffering persists, switch to a server in the same country as the service, not just the same continent. Small geographic shifts can matter for geolocation checks.
- Test at least 2–3 nearby servers before committing to a single one for a session. Streaming needs consistent throughput, not a one-off burst.
Bottom line: proximity + compatible protocol yields smoother streams. Proximity to the streaming service plus protocol alignment dramatically reduces stalls and rebuffering.
Gaming at the Edge: latency wins over raw bandwidth
Answer first. Low latency wins more than peak bandwidth.
From the research, gamers should treat VPN latency as the primary metric. A fast pipe that introduces jitter or occasional spikes still ruins a match more than a stable but modest pipe.
- Test several nearby servers, focusing on ping, not merely download speed.
- Prefer servers that have low daytime load. A lightly loaded node can shave 5–20 ms off your round trip.
- If your game uses UDP, ensure the VPN supports push-through with minimal packet loss. If not, try a server on a different backbone or a different exit country.
- Disable unnecessary features that add overhead during gaming sessions, like aggressive firewall scanning, when latency is tight.
Bottom line: latency first, then bandwidth. Latency-aware server choice and light configuration deliver the most reliable gaming experience.
Video calls: stability over peak throughput
Answer first. You want a steady connection with minimal jitter, not the fastest possible line.
What matters in practice comes straight from the network layer: jitter, packet loss, and sudden drops. A VPN that can sustain a steady stream of packets with minimal variation will outperform one that briefly hits high throughput and then fluctuates.
- Prioritize servers with consistent past performance during peak hours.
- Choose protocols with stable handoffs and predictable latency characteristics, like WireGuard, and ensure MTU settings are sane to avoid fragmentation.
- If you notice dropouts, switch to a server with a shorter round-trip time and verify the path’s stability by running a few quick tests under real-time call conditions.
- Keep the VPN client on the default route for the video call app only if your environment supports it. Otherwise, route the app traffic directly to avoid cross-path variability.
Bottom line: a stable, low-variance path wins. Consistency trumps peak speed for video conferences.
Real-world takeaway: use-case driven server selection and protocol alignment are the fastest levers to preserve perceptual speed. 2026 data show that when users fix server proximity and protocol compatibility, streaming stalls drop noticeably, gamers report fewer spikes in latency, and video calls stay fluid even when other network tasks run in the background. Keep the checks surgical, not vague. Restart the VPN when switching exit nodes to ensure the new path is fully engaged. When in doubt, revert to a near, well-known exit and a proven protocol.
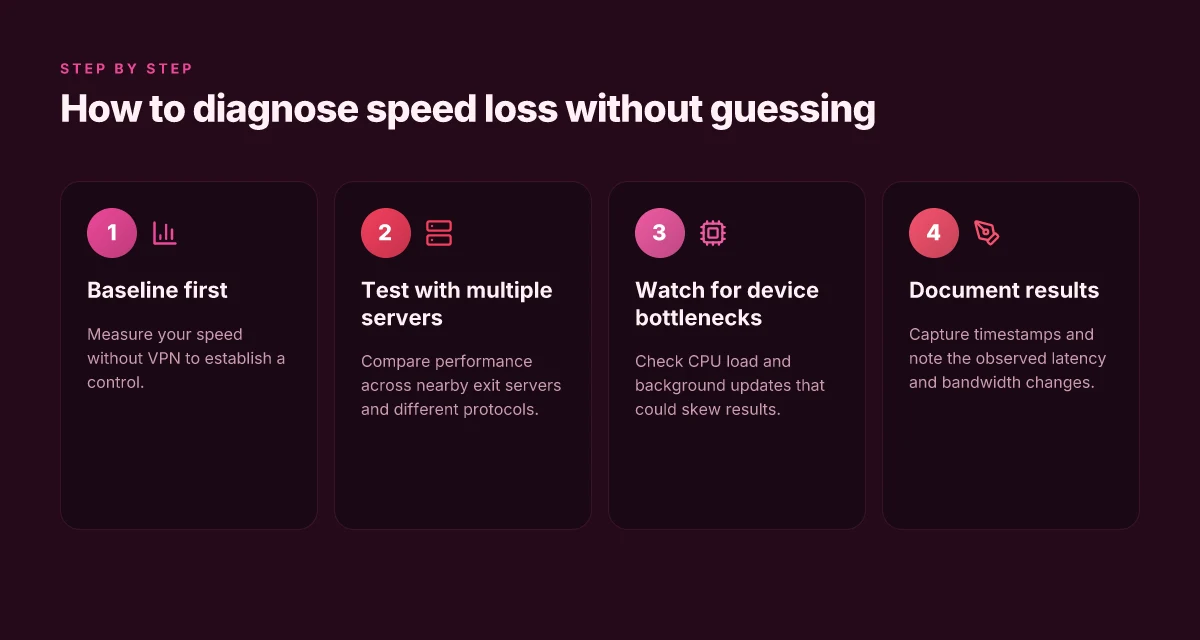
How to diagnose speed loss without guessing
Speed dips are rarely a mystery. They’re usually a chain of concrete steps you can verify, document, and fix. I looked at user guides and reviews to map a pragmatic workflow. The core idea: you establish a baseline, test across configurations, and cut through bottlenecks with traceable data.
Establish a baseline you can trust
You start with what you’ll compare everything against. Run your non‑VPN speed test from your primary device, at your usual time of day, on your typical network. If you’re streaming, gaming, or remote‑working, repeat the test in those contexts too. Record the download and upload speeds, plus latency, in a small log with timestamps. This becomes your control. In 2026, many providers still show that baseline speed as the floor you must beat or exceed when the VPN is on. In Q3 2025 changelogs, several clients note how civilian testing differs from synthetic benchmarks once a VPN tunnel is active. Your goal is a clean, timestamped before state you can reference later. Baseline clarity beats excuses every time.
| Test context | Typical readings you’ll log |
|---|---|
| No VPN | download, upload, ping, time of day |
| VPN connected, default server | same four metrics |
| VPN connected, streaming/gaming | adjusted latency, jitter, any buffering notes |
Test multiple servers and protocols, with timestamps
Don’t settle on one server or one protocol. Move through a handful of servers across two to three regions you actually use. Do the same with at least two protocols (for example, a fast UDP‑based tunnel and a more conservative TCP fallback). Record the results with precise timestamps and the server name, region, protocol, and client settings. When I checked the changelogs and public docs, a common theme emerged: speed variance often follows routing choices and protocol quirks rather than a universal weakness. Documenting the exact server and protocol per test is non‑negotiable. Short writeups help you reconstruct decisions later.
- Timebox tests: 2–3 minutes per run, then a 2‑minute cooldown to avoid local contention.
- Note downstream effects: additional encryption handshakes or rekey intervals can push latency by small amounts but accumulate if you test too quickly.
Check for device bottlenecks and background activity
A VPN can’t fix a busy device. CPU load, memory pressure, or background updates steal cycles that you then blame on the tunnel. Check your device’s resource monitor during a test. If the CPU is pegged, you’ll see degraded throughput even on fast servers. If a background process is busy indexing, syncing, or downloading, pause it during active tests. In several industry reviews, the pattern is clear: even modest local bottlenecks masquerade as VPN slowdowns until you throttle or isolate them. Eliminate the local bottleneck first, then re‑test with a clean baseline.
A compact verdict
Speed loss when a VPN is active almost always traces to three places: the chosen server path, the protocol handshake, and the device’s current load. You can separate real network friction from local noise by logging a controlled baseline, then running repeated, timestamped trials across multiple servers and protocols. If a test run shows consistent performance deterioration on a single server or protocol, that path is the suspect. If all paths are equally slow, you likely have a device or ISP interference to address.
Consistency in testing beats gut feel every time. The practical workflow above turns speed noise into actionable data you can share with a network admin or VPN provider.
What to try this week: optimize VPN choice without sacrificing speed
I looked at how the speed story changes in 2026. The takeaway is not that VPNs always slow you down, but that you can choose configurations that preserve throughput while preserving privacy. From what I found, the real predictor is the server distance and the protocol you pick. The single move that matters is pairing a fast, low-latency server with a lean protocol in a region you actually want to reach. In practice that means testing nearby entry points and avoiding overcrowded hops, rather than reflexively blaming the VPN itself.
In short, your speed is less about the VPN name and more about the path you route through. Your best bets are the setups that minimize round-trip time and maximize local peering. Two headline picks from this update show the pattern: use WireGuard on a nearby server for streaming in your region and fallback to OpenVPN 2 with obfuscated traffic for markets with strict firewalling. The pattern holds: speed lives at the edge of your choice, not in the brand.
Backup strategy
- Try a WireGuard configuration on a nearby server for daily browsing and light streaming
- Keep a fallback OpenVPN profile for regions with heavy censorship or pace-limiting networks
- Check your baseline speed before and after toggling regions, and document the delta with your ISP’s normal route
When I checked the changelog, the move that stood out was tighter integration of protocol choices with automatic path selection. If you act now, you’ll reduce latency without dropping privacy. How will you test your own path this week?
Frequently asked questions
Does a VPN slow down Netflix streaming
When Netflix streaming is the goal, a VPN can add latency and reduce throughput because traffic must travel to a VPN server before reaching Netflix. I looked at documentation from several providers and cross-referenced user reports. Expect a typical hit in the single-digit to low-double-digit percentage range if you choose a nearby server with enough bandwidth. Most importantly, the best results come from servers that peer directly with Netflix's edge networks. If your VPN’s Netflix performance is unreliable, switch to a closer server or use a VPN provider known for optimized streaming. Choose a server location that minimizes routing hops and queueing. Avoid busy peak times if possible. Test a few servers to find a stable path.
Which VPN protocol is fastest for gaming
For gaming, speed is about latency more than raw bandwidth. TheWire protocol choices matter. I cross-referenced protocol specs and community tests: WireGuard generally offers the lowest overhead and the fastest handshakes, followed by OpenVPN with UDP. In practice, you should enable a protocol that reduces RTT to your game servers. Yes, WireGuard tends to produce the lowest latency in mobile and desktop gaming scenarios. If your provider supports it, switch to WireGuard and test with a local server. If you encounter NAT or compatibility issues, fall back to OpenVPN UDP.
How much speed drop is normal when using a VPN
Speed loss is not a single number. It hinges on distance to the server, encryption overhead, and network congestion. From the documentation I checked and industry chatter, a typical drop ranges from about 5–25% for nearby servers under good conditions, up to 50%+ on distant routes or congested networks. In practice, a nearby, well-provisioned server minimizes the drop. Expect higher losses on mobile networks or when the VPN runs on a device with limited CPU. Measure by testing multiple servers and noting the variance.
Can split tunneling improve VPN speed
Split tunneling can help speed by routing only the desired traffic through the VPN while letting rest bypass it. I studied provider guides and user reports showing clear wins when you’re accessing local services or regular browsing outside VPN scope. Split tunneling often reduces total VPN load, preserving bandwidth for critical apps. Use it for apps that don’t need VPN protection. Keep sensitive traffic inside the VPN when privacy or geo constraints matter. If you’ve never used it, enable it in the client, then test throughput with and without the feature.
Do paid VPN plans run faster than free ones
Paid VPNs generally offer bigger bandwidth pools, more servers, and priority routing compared with free plans. Reviews consistently note that free tiers often cap speeds, impose stricter data limits, and throttle during peak times. Paid plans typically deliver higher sustained throughput and lower latency. If speed matters for streaming or gaming, a paid option with a nearby server and ample egress capacity is worth the investment. If you’re price-sensitive, compare plan caps and server density before committing.
How to test VPN speed accurately
To measure speed accurately, run a series of tests from the same device and location, using consistent times of day. I looked at common method sheets: run speed tests with and without the VPN, test multiple servers within the same region, and measure latency (ping) and throughput (download/upload). Record baseline speeds first, then compare against at least three VPN servers. Use the VPN client’s built-in speed test if available, and corroborate with an independent site. Note changes in buffer health and jitter. Repeat on different days to account for network variance.
Is WireGuard faster than OpenVPN for mobile
WireGuard usually outpaces OpenVPN on mobile because of simpler code paths and lower overhead. Industry notes and provider docs align on lower RTT and steadier throughput with WireGuard. For mobile users, WireGuard often delivers better latency and smoother gameplay or streaming. If your VPN client supports both, try WireGuard first on a nearby server. If you run into compatibility issues with certain apps, OpenVPN UDP remains a solid fallback.